
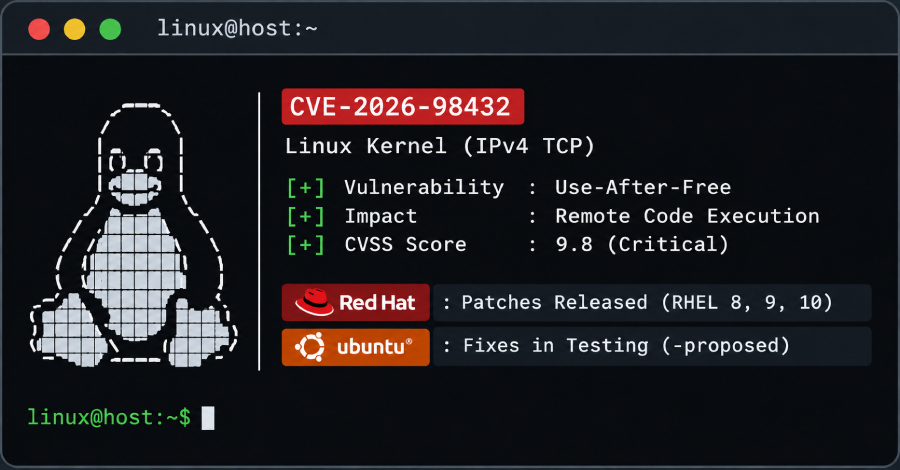
Fixed kernels for a use-after-free vulnerability in the Linux kernel’s IPv4 TCP code are now available for Red Hat Enterprise Linux 8, 9, and 10, while Ubuntu’s fixes for its three newest long-term-support releases remain in its opt-in testing channel with no date for a regular update.
The flaw, tracked as CVE-2026-98432, can be reached by a remote, unauthenticated attacker and can…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment