
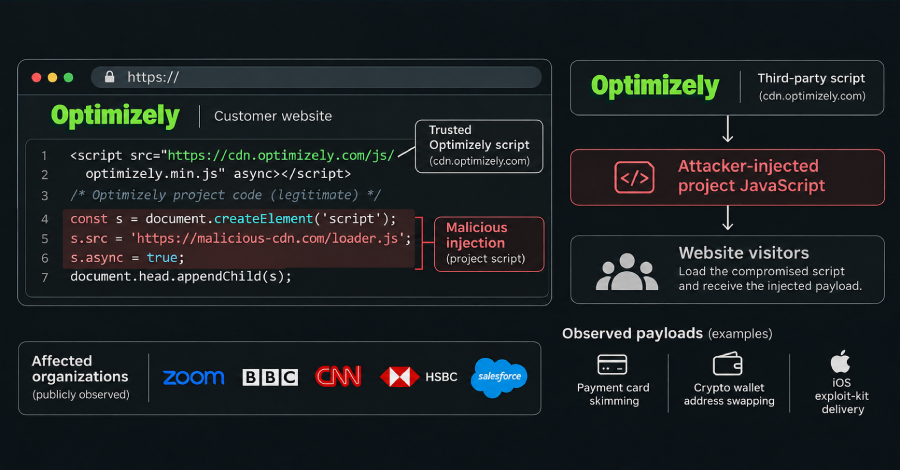
An attacker exploited a flaw in Optimizely Web Experimentation to plant malicious code in some of the scripts that customers’ websites load from the service, Optimizely said early today.
Visitors to sites run by at least 178 organizations, including CNN, the BBC and Zoom, received the code yesterday, according to Report URI, a firm that monitors the scripts websites run.
The code was built to…
Read the rest of the story at Read More
Source: The Hacker News


Recent News


Leave a Comment