





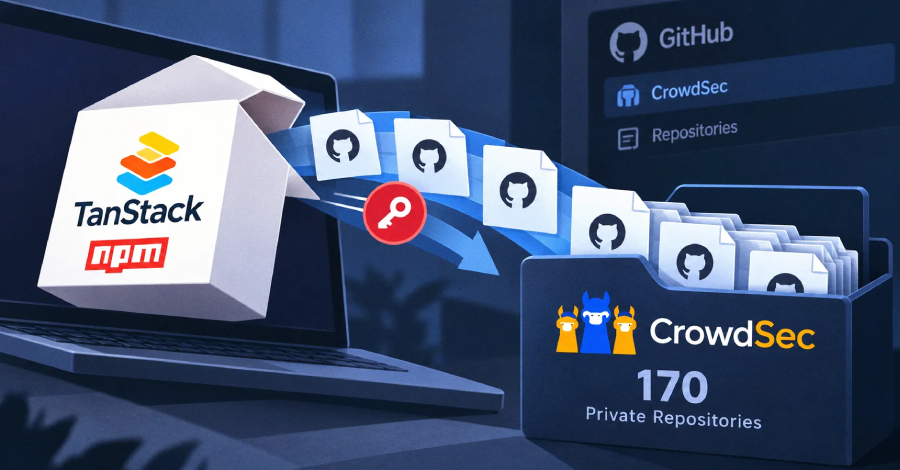
An attacker copied about 170 of CrowdSec’s private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18.
The French security company had kept his GitHub access open. CrowdSec says his laptop was compromised in May’s supply chain attack on TanStack, in which malicious versions of TanStack’s npm packages stole credentials from…
Read the rest of the story at Read More
Source: The Hacker News


Recent News


Leave a Comment