
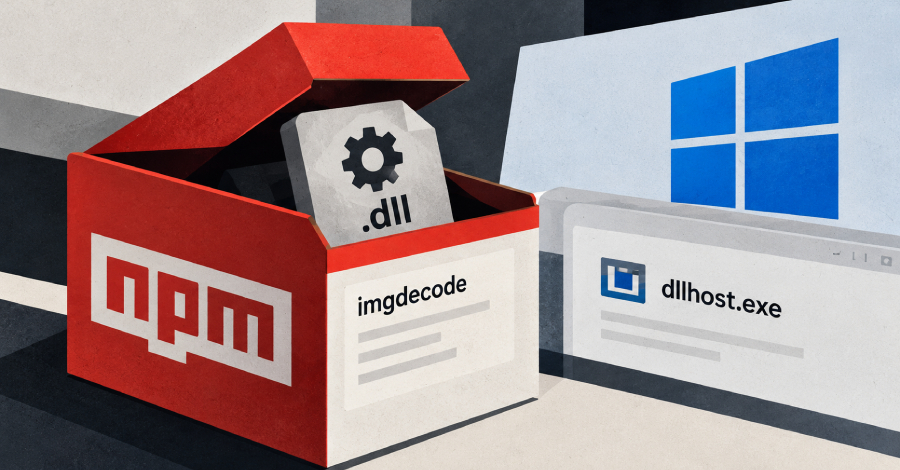
Cybersecurity researchers have discovered a malicious npm package that’s part of a recently disclosed software supply chain attack campaign dubbed MALFEX.
The package, named “imgdecode,” was uploaded to the package registry on September 30, 2026, by a user named “malfexteste8.” It has been downloaded 979 times as of writing and is still available on npm as of writing. The latest version of…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment