PyPI Packages Deliver ZiChatBot Malware via Zulip APIs on Windows and Linux

Cybersecurity researchers have discovered three packages on the Python Package Index (PyPI) repository that are designed to stealthily deliver a previously unknown malware family called ZiChatBot on Windows and Linux systems. “While these wheel packages do implement the features described on
vm2 Node.js Library Vulnerabilities Enable Sandbox Escape and Arbitrary Code Execution

A dozen critical security vulnerabilities have been disclosed in the vm2 Node.js library that could be exploited by bad actors to break out of the sandbox and execute arbitrary code on susceptible systems. vm2 is an open-source library used to

Mirai-Based xlabs_v1 Botnet Exploits ADB to Hijack IoT Devices for DDoS Attacks

Cybersecurity researchers have exposed a new Mirai-derived botnet that self-identifies as xlabs_v1 and targets internet-exposed devices running Android Debug Bridge (ADB) to enlist them in a network capable of carrying out distributed denial-of-service (DDoS) attacks. Hunt.io, which detailed the malware,

MuddyWater Uses Microsoft Teams to Steal Credentials in False Flag Ransomware Attack

The Iranian state-sponsored hacking group known as MuddyWater (aka Mango Sandstorm, Seedworm, and Static Kitten) has been attributed to a ransomware attack in what has been described as a “false flag” operation. The attack, observed by Rapid7 in early 2026,

The Hacker News Launches ‘Cybersecurity Stars Awards 2026’ — Submissions Now Open

For nearly 20 years, we at The Hacker News have mostly told scary stories about cyberspace — big hacks, broken systems, and new threats. But behind every headline, there’s a quieter, better story. It’s the story of leaders making tough

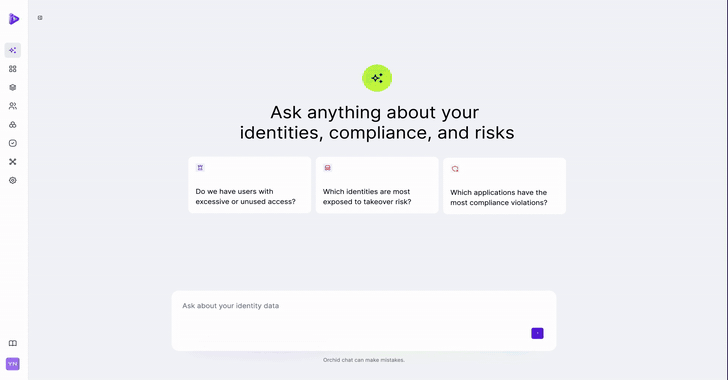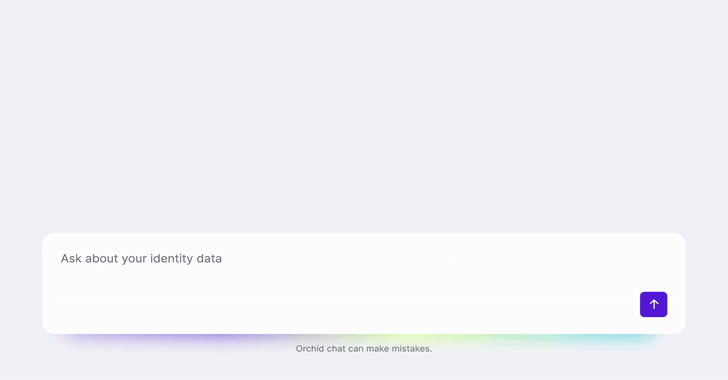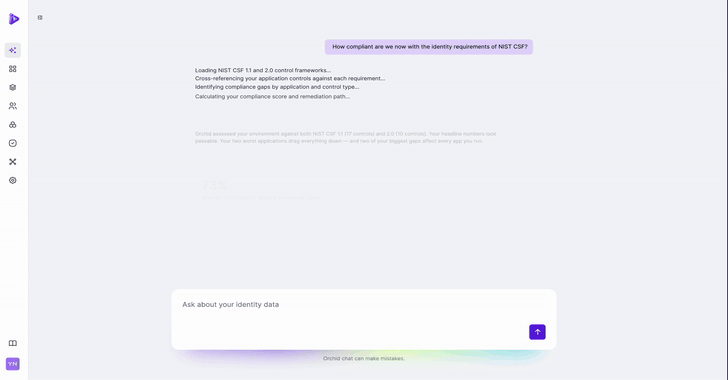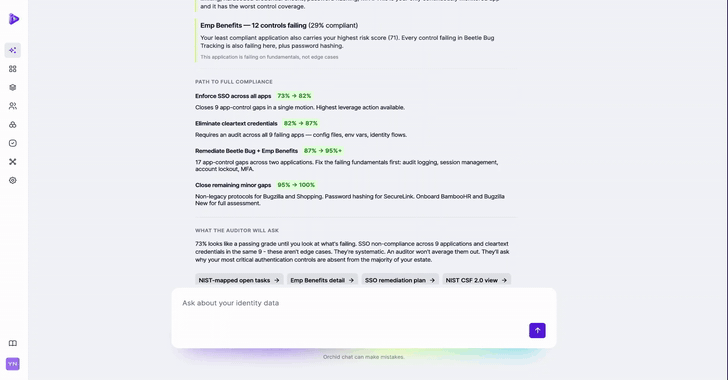
Your AI Agents Are Already Inside the Perimeter. Do You Know What They’re Doing?

Analysts recently confirmed what identity security teams have quietly feared: AI agents are being deployed faster than enterprises can govern them. In their inaugural Market Guide for Guardian Agents, Gartner states that “enterprise adoption of AI agents is accelerating, outpacing

Google’s Android Apps Get Public Verification to Stop Supply Chain Attacks

Google has announced expanded Binary Transparency for Android as a way to safeguard the ecosystem from supply chain attacks. “This new public ledger ensures the Google apps on your device are exactly what we intended to build and distribute,” Google’s

Windows Phone Link Exploited by CloudZ RAT to Steal Credentials and OTPs

Cybersecurity researchers have disclosed details of an intrusion that involved the use of a CloudZ remote access tool (RAT) and a previous undocumented plugin dubbed Pheno with the aim of facilitating credential theft. “According to the functionalities of the CloudZ

Palo Alto PAN-OS Flaw Under Active Exploitation Enables Remote Code Execution

Palo Alto Networks has released an advisory warning that a critical buffer overflow vulnerability in its PAN-OS software has been exploited in the wild. The vulnerability, tracked as CVE-2026-0300, has been described as a case of unauthenticated remote code execution.

Critical Apache HTTP/2 Flaw (CVE-2026-23918) Enables DoS and Potential RCE

The Apache Software Foundation (ASF) has released security updates to address several security vulnerabilities in the HTTP Server, including a severe vulnerability that could potentially lead to remote code execution (RCE). The vulnerability, tracked as CVE-2026-23918 (CVSS score: 8.8), has