Attackers Exploit Critical JFrog Artifactory Flaw to Mint Admin Tokens Days After Disclosure

Threat actors are exploiting a newly patched critical security flaw impacting JFrog Artifactory merely days after public disclosure, according to watchTowr. The vulnerability in question is CVE-2026-82329 (CVSS score: 9.8), a case of authentication bypass that could lead to administrative
Breeze Comet Executes Hundreds of Fraudulent Transactions via Brazilian Payment Systems

Brazilian financial services, retail, and e-commerce organizations have become the target of a financially motivated threat actor dubbed Breeze Comet (formerly UNC5669) since 2024. Google Threat Intelligence Group (GTIG) and Mandiant teams described the threat actor as “specializing in manipulating

13 Malicious Packagist Packages Target Unpatched iPhones to Steal Crypto Wallet Seeds

Cybersecurity researchers have identified a set of 13 malicious Composer theme packages on Packagist that are designed to inject JavaScript into Vietnamese movie and comic streaming sites that install those libraries and initiate the deployment of spyware aimed at unpatched

Iranian Hackers Pose as Recruiters to Deliver Cross-Platform RATs Through Coding Tests

The Iranian Nimbus Manticore hacking group has been attributed to two previously undocumented malware families that highlight the continued evolution of its toolset and likely expand its targeting footprint to infect Linux and Apple macOS systems using cross-platform remote access

Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones

The most common way into a company last year was to ask. A web page tells the visitor to prove they are not a robot. While they read the instructions, it quietly places a command on their clipboard. Then it

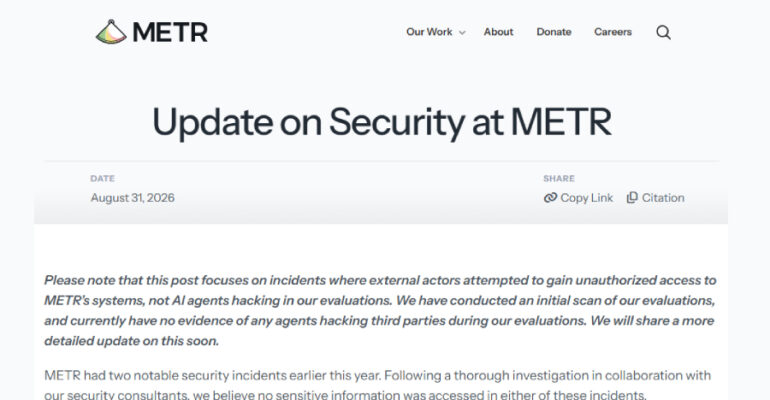
Attackers Steal METR API Key and Consume AI Credits Worth About $600,000

METR (short for Model Evaluation and Threat Research and pronounced “Meter”), a research non-profit that evaluates frontier artificial intelligence (AI) models for their ability to carry out long-horizon, agentic tasks, disclosed that it suffered “two notable security incidents” where external

Russia-Aligned UAC-0099 Plants Nuclear Weapon Prompt in Malware to Disrupt AI Analysis

Cybersecurity researchers have disclosed a new technique dubbed GuardBreaker that’s been put to use by a Russia-aligned threat actor known as UAC-0099 against a target in Ukraine with an aim to interfere with artificial intelligence (AI)-assisted analysis. The idea, ESET

Attackers Exploit Critical Langflow and Rails Flaws in Credential-Probing and C2 Activity

Threat actors are exploiting two critical flaws impacting Langflow and Ruby on Rails, according to new findings from VulnCheck. The vulnerabilities in question are listed below – CVE-2026-0768 (CVSS score: 9.8) – A lack of proper validation of a user-supplied

North Korean Job Fraud Expands Beyond IT Into Healthcare and Sales

Threat actors with ties to the Democratic People’s Republic of Korea (aka DPRK or North Korea) have been observed seeking job opportunities beyond the information technology (IT) sector, with recent investigations identifying suspected workers employed in sales and marketing and

⚡ Weekly Recap: Chinese Spy Proxy, AI Agents Go Off-Task, Router Backdoors and More

The boring parts caused most of the trouble. A router shipped ready to listen. A fake check turned the user into the installer. Trusted systems collected traffic and passwords, then cleaned the logs. Old bugs formed new attack chains. Even