ValleyRAT Backdoor Hides in Signed Adware That Users Add to Antivirus Exclusions

The threat actor known as Silver Fox has been observed distributing the ValleyRAT backdoor disguised as a signed Chinese adware application, running the malware under a trusted process to slip past users who add such software to their antivirus exclusions.
Aurora Ransomware Operators Use Cursor AI in Attacks Against 10 Targets

Threat actors associated with Aurora (aka Aur0ra) ransomware have been observed using SpaceX’s artificial intelligence (AI)-powered coding assistant Cursor to break into target networks, according to findings from CloudSEK and Gambit Security. The two independent analyses are based on exposed

Securing Claude Code: The New Compliance API, Local Visibility, and Identity Governance

Claude Code reads files, runs shell commands, invokes MCP tools, and acts through the credentials available on a developer’s machine. Anthropic’s new Compliance API endpoints give security teams their clearest view yet into that activity. They also expose a larger

China-Linked Fire Ant Hijacks Cisco Routers to Steal Credentials and Blind Security Logs

A China-nexus cyber espionage actor tracked as Fire Ant has expanded a long-running campaign beyond VMware hypervisors to compromise Cisco IOS XR routers, Terminal Access Controller Access-Control System (TACACS) servers, and Linux management hosts used to route, authenticate, and manage

DoJ Corrects China Hacking Claim, Says U.S. Agencies Were Targets, Not Victims

The U.S. Department of Justice (DoJ) on Friday corrected a previously issued press statement that several of its agencies were victims of attacks carried out by Chinese threat actors, instead now pointing out that they were among those targeted. Last

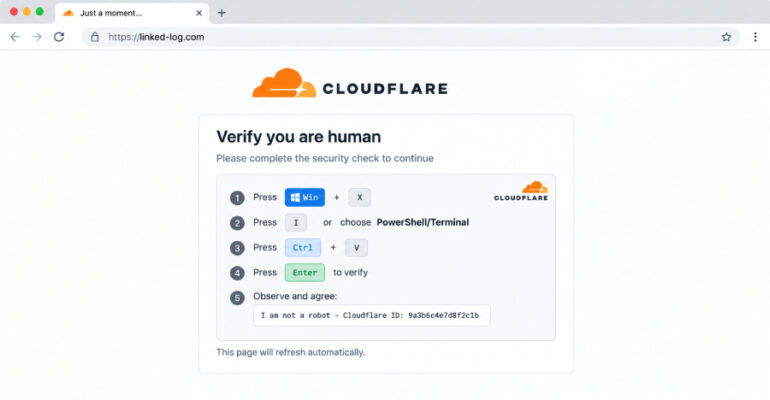
TerminalFix Uses Fake Cloudflare CAPTCHAs to Deploy Reverse-Tunnel Backdoor

Microsoft has disclosed details of a new ClickFix variant, dubbed TerminalFix, that aims to trick users into running a malicious command in Windows Terminal or PowerShell. “While traditional ClickFix campaigns direct victims to the Windows Run dialog, TerminalFix campaigns apply

Five Critical WordPress Plugin and Theme Flaws Enable Site Takeover or RCE

Multiple critical security flaws have been disclosed in WordPress plugins and themes, including WPMU DEV Dashboard, Avada, TranslatePress, Pods, and GiveWP, that could lead to authentication bypass, account takeover, and arbitrary code execution. The vulnerabilities, according to Wordfence and Patchstack,

Berlin Refuses to Pay Hackers Who Stole Data From the City’s State Network

Berlin’s state government has confirmed that it is the target of an extortion attempt following the August compromise of the city’s state administrative network, and said it will not meet the extortionists’ demands. The same statement disclosed that forensic work

Cosmos EVM Flaw Exploited After Cosmos Labs Knew Every Blockchain Running It Was Vulnerable

Cosmos Labs has warned that a critical balance-handling flaw in the shared Cosmos EVM module was exploited to drain funds from six blockchains between August 20 and August 25, 2026. The vulnerability, designated GHSA-7g4w-cg88-2cq2, is rated Critical by Cosmos Labs

Attackers Chain Two PaperCut Flaws to Execute Code Without Authentication

Malicious actors are exploiting a newly patched security flaw in PaperCut NG and MF to execute arbitrary code on susceptible instances, as the company released a fresh emergency fix with additional hardening. “This vulnerability gives an unauthenticated attacker remote control