Malvertising Scam Uses Fake Google Ads to Hijack Microsoft Advertising Accounts

Cybersecurity researchers have discovered a malvertising campaign that’s targeting Microsoft advertisers with bogus Google ads that aim to take them to phishing pages that are capable of harvesting their credentials. “These malicious ads, appearing on Google Search, are designed to
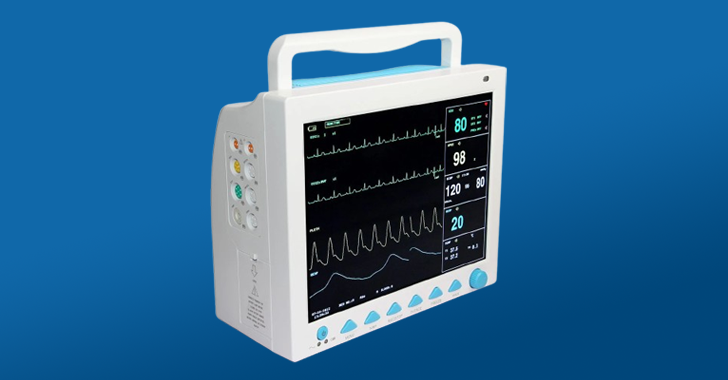
CISA and FDA Warn of Critical Backdoor in Contec CMS8000 Patient Monitors

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) and the Food and Drug Administration (FDA) have issued alerts about the presence of hidden functionality in Contec CMS8000 patient monitors and Epsimed MN-120 patient monitors. The vulnerability, tracked as CVE-2025-0626, carries

Top 5 AI-Powered Social Engineering Attacks

Social engineering has long been an effective tactic because of how it focuses on human vulnerabilities. There’s no brute-force ‘spray and pray’ password guessing. No scouring systems for unpatched software. Instead, it simply relies on manipulating emotions such as trust,

Italy Bans Chinese DeepSeek AI Over Data Privacy and Ethical Concerns

Italy’s data protection watchdog has blocked Chinese artificial intelligence (AI) firm DeepSeek’s service within the country, citing a lack of information on its use of users’ personal data. The development comes days after the authority, the Garante, sent a series

Google Bans 158,000 Malicious Android App Developer Accounts in 2024

Google said it blocked over 2.36 million policy-violating Android apps from being published to the Google Play app marketplace in 2024 and banned more than 158,000 bad developer accounts that attempted to publish such harmful apps. The tech giant also

Broadcom Patches VMware Aria Flaws – Exploits May Lead to Credential Theft

Broadcom has released security updates to patch five security flaws impacting VMware Aria Operations and Aria Operations for Logs, warning customers that attackers could exploit them to gain elevated access or obtain sensitive information. The list of identified flaws, which

Google: Over 57 Nation-State Threat Groups Using AI for Cyber Operations

Over 57 distinct threat actors with ties to China, Iran, North Korea, and Russia have been observed using artificial intelligence (AI) technology powered by Google to further enable their malicious cyber and information operations. “Threat actors are experimenting with Gemini

Authorities Seize Domains of Popular Hacking Forums in Major Cybercrime Crackdown

An international law enforcement operation has dismantled the domains associated with various online platforms linked to cybercrime such as Cracked, Nulled, Sellix, and StarkRDP. The effort has targeted the following domains – www.cracked.io www.nulled.to www.mysellix.io www.sellix.io www.starkrdp.io Visitors to these

Lightning AI Studio Vulnerability Allowed RCE via Hidden URL Parameter

Cybersecurity researchers have disclosed a critical security flaw in the Lightning AI Studio development platform that, if successfully exploited, could allow for remote code execution. The vulnerability, rated a CVSS score of 9.4, enables “attackers to potentially execute arbitrary commands

SOC Analysts – Reimagining Their Role Using AI

The job of a SOC analyst has never been easy. Faced with an overwhelming flood of daily alerts, analysts (and sometimes IT teams who are doubling as SecOps) must try and triage thousands of security alerts—often false positives—just to identify