Zyxel CPE Devices Face Active Exploitation Due to Unpatched CVE-2024-40891 Vulnerability

Cybersecurity researchers are warning that a critical zero-day vulnerability impacting Zyxel CPE Series devices is seeing active exploitation attempts in the wild. “Attackers can leverage this vulnerability to execute arbitrary commands on affected devices, leading to complete system compromise, data
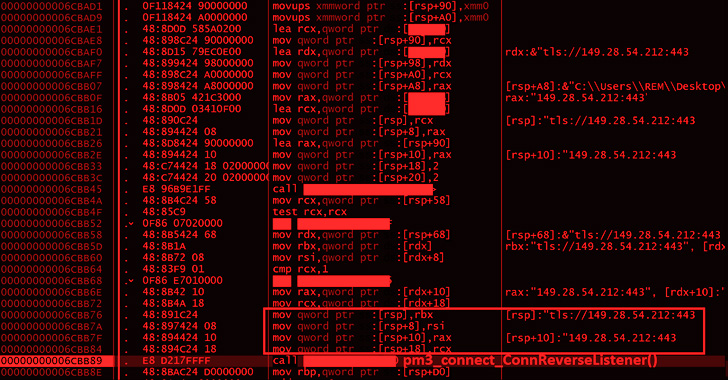
PureCrypter Deploys Agent Tesla and New TorNet Backdoor in Ongoing Cyberattacks

A financially motivated threat actor has been linked to an ongoing phishing email campaign that has been ongoing since at least July 2024 specifically targeting users in Poland and Germany. The attacks have led to the deployment of various payloads,

OAuth Redirect Flaw in Airline Travel Integration Exposes Millions to Account Hijacking

Cybersecurity researchers have disclosed details of a now-patched account takeover vulnerability affecting a popular online travel service for hotel and car rentals. “By exploiting this flaw, attackers can gain unauthorized access to any user’s account within the system, effectively allowing

AI SOC Analysts: Propelling SecOps into the future

Triaging and investigating alerts is central to security operations. As SOC teams strive to keep up with ever-increasing alert volumes and complexity, modernizing SOC automation strategies with AI has emerged as a critical solution. This blog explores how an AI

Ransomware Targets ESXi Systems via Stealthy SSH Tunnels for C2 Operations

Cybersecurity researchers have found that ransomware attacks targeting ESXi systems are also leveraging the access to repurpose the appliances as a conduit to tunnel traffic to command-and-control (C2) infrastructure and stay under the radar. “ESXi appliances, which are unmonitored, are

How Long Does It Take Hackers to Crack Modern Hashing Algorithms?

While passwords remain the first line of defense for protecting user accounts against unauthorized access, the methods for creating strong passwords and protecting them are continually evolving. For example, NIST password recommendations are now prioritizing password length over complexity. Hashing,

E.U. Sanctions 3 Russian Nationals for Cyber Attacks Targeting Estonia’s Key Ministries

The Council of the European Union has sanctioned three individuals for allegedly carrying out “malicious cyber activities” against Estonia. The three Russian nationals – Nikolay Alexandrovich Korchagin, Vitaly Shevchenko, and Yuriy Fedorovich Denisov – are officers of the General Staff

Top-Rated Chinese AI App DeepSeek Limits Registrations Amid Cyberattacks

DeepSeek, the Chinese AI startup that has captured much of the artificial intelligence (AI) buzz in recent days, said it’s restricting registrations on the service, citing malicious attacks. “Due to large-scale malicious attacks on DeepSeek’s services, we are temporarily limiting

Apple Patches Actively Exploited Zero-Day Affecting iPhones, Macs, and More

Apple has released software updates to address several security flaws across its portfolio, including a zero-day vulnerability that it said has been exploited in the wild. The vulnerability, tracked as CVE-2025-24085, has been described as a use-after-free bug in the

GitHub Desktop Vulnerability Risks Credential Leaks via Malicious Remote URLs

Multiple security vulnerabilities have been disclosed in GitHub Desktop as well as other Git-related projects that, if successfully exploited, could permit an attacker to gain unauthorized access to a user’s Git credentials. “Git implements a protocol called Git Credential Protocol