Chinese Hackers Use GHOSTSPIDER Malware to Hack Telecoms Across 12+ Countries

The China-linked threat actor known as Earth Estries has been observed using a previously undocumented backdoor called GHOSTSPIDER as part of its attacks targeting Southeast Asian telecommunications companies.  Trend Micro, which described the hacking group as an aggressive advanced persistent
CISA Urges Agencies to Patch Critical “Array Networks” Flaw Amid Active Attacks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a now-patched critical security flaw impacting Array Networks AG and vxAG secure access gateways to its Known Exploited Vulnerabilities (KEV) catalog following reports of active exploitation in the wild.

Google’s New Restore Credentials Tool Simplifies App Login After Android Migration

Google has introduced a new feature called Restore Credentials to help users restore their account access to third-party apps securely after migrating to a new Android device. Part of Android’s Credential Manager API, the feature aims to reduce the hassle

PyPI Python Library “aiocpa” Found Exfiltrating Crypto Keys via Telegram Bot

The administrators of the Python Package Index (PyPI) repository have quarantined the package “aiocpa” following a new update that included malicious code to exfiltrate private keys via Telegram. The package in question is described as a synchronous and asynchronous Crypto

Flying Under the Radar – Security Evasion Techniques

Dive into the evolution of phishing and malware evasion techniques and understand how attackers are using increasingly sophisticated methods to bypass security measures. The Evolution of Phishing Attacks “I really like the saying that ‘This is out of scope’ said

Cybersecurity Blind Spots in IaC and PaC Tools Expose Cloud Platforms to New Attacks

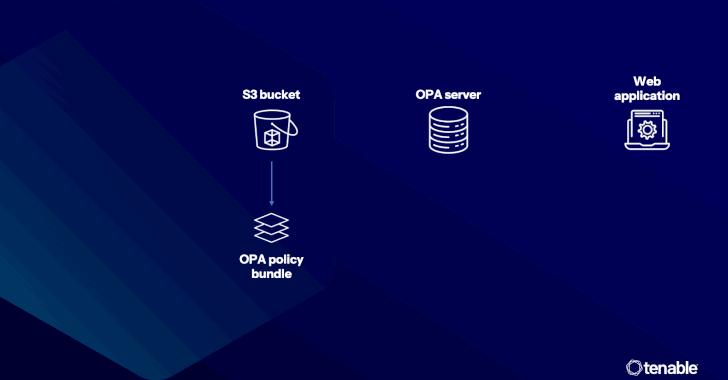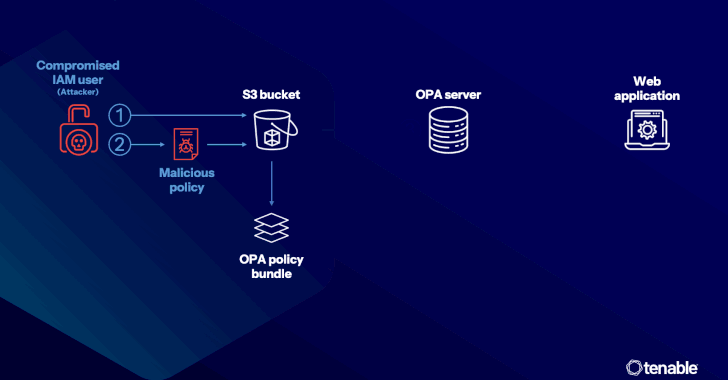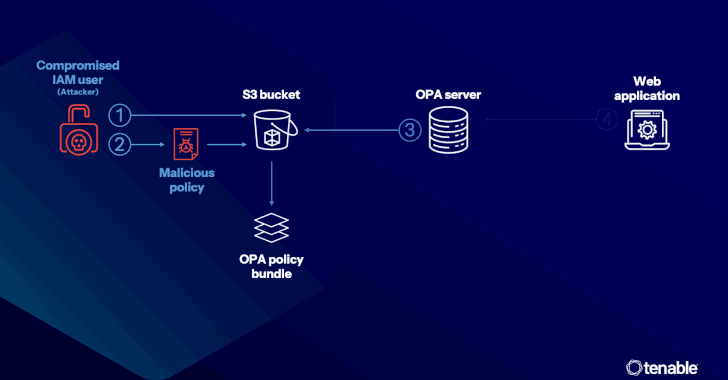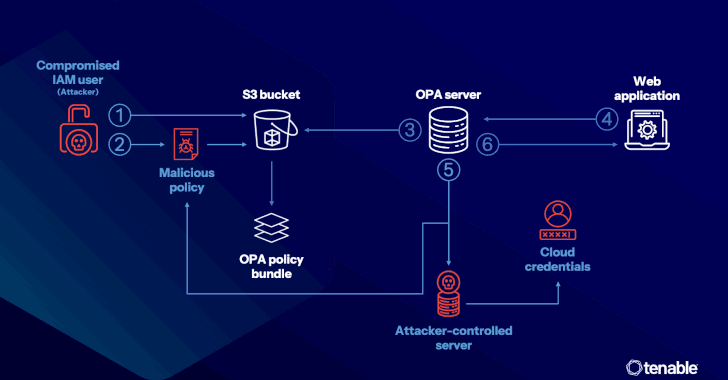
Cybersecurity researchers have disclosed two new attack techniques against infrastructure-as-code (IaC) and policy-as-code (PaC) tools like HashiCorp’s Terraform and Open Policy Agent (OPA) that leverage dedicated, domain-specific languages (DSLs) to breach cloud platforms and exfiltrate data. “Since these are hardened

THN Recap: Top Cybersecurity Threats, Tools, and Practices (Nov 18 – Nov 24)

We hear terms like “state-sponsored attacks” and “critical vulnerabilities” all the time, but what’s really going on behind those words? This week’s cybersecurity news isn’t just about hackers and headlines—it’s about how digital risks shape our lives in ways we

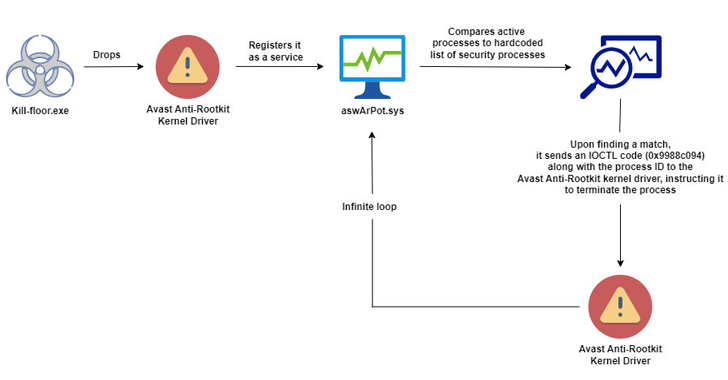
Researchers Uncover Malware Using BYOVD to Bypass Antivirus Protections

Cybersecurity researchers have uncovered a new malicious campaign that leverages a technique called Bring Your Own Vulnerable Driver (BYOVD) to disarm security protections and ultimately gain access to the infected system. “This malware takes a more sinister route: it drops

Google Exposes GLASSBRIDGE: A Pro-China Influence Network of Fake News Sites

Government agencies and non-governmental organizations in the United States have become the target of a nascent China state threat actor known as Storm-2077. The adversary, believed to be active since at least January 2024, has also conducted cyber attacks against

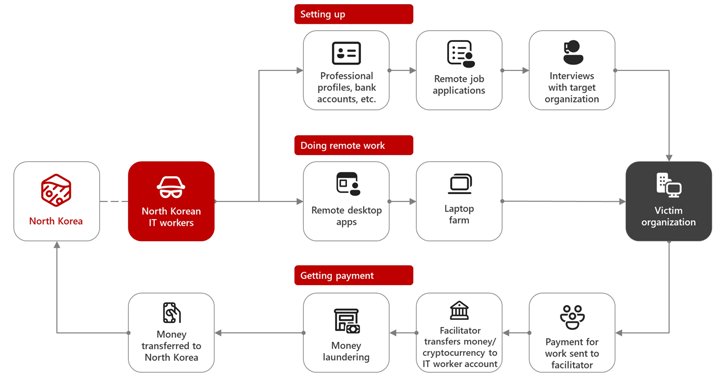
North Korean Hackers Steal $10M with AI-Driven Scams and Malware on LinkedIn

The North Korea-linked threat actor known as Sapphire Sleet is estimated to have stolen more than $10 million worth of cryptocurrency as part of social engineering campaigns orchestrated over a six-month period. These findings come from Microsoft, which said that