China-Linked TAG-112 Targets Tibetan Media with Cobalt Strike Espionage Campaign

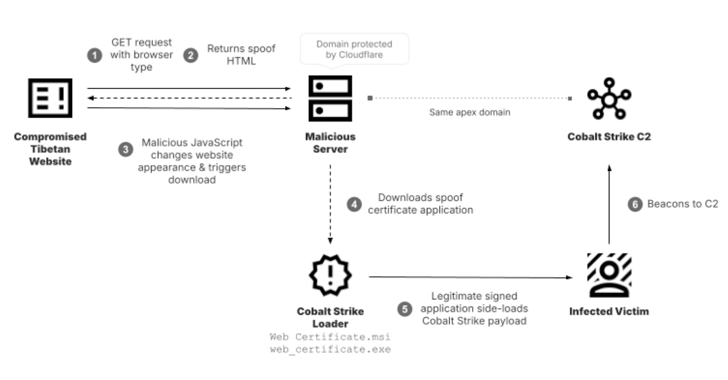
A China-linked nation-state group called TAG-112 compromised Tibetan media and university websites in a new cyber espionage campaign designed to facilitate the delivery of the Cobalt Strike post-exploitation toolkit for follow-on information collection. “The attackers embedded malicious JavaScript in these
Russian Hackers Deploy HATVIBE and CHERRYSPY Malware Across Europe and Asia

Threat actors with ties to Russia have been linked to a cyber espionage campaign aimed at organizations in Central Asia, East Asia, and Europe. Recorded Future’s Insikt Group, which has assigned the activity cluster the name TAG-110, said it overlaps

Unlocking Google Workspace Security: Are You Doing Enough to Protect Your Data?

Google Workspace has quickly become the productivity backbone for businesses worldwide, offering an all-in-one suite with email, cloud storage and collaboration tools. This single-platform approach makes it easy for teams to connect and work efficiently, no matter where they are,

Microsoft, Meta, and DOJ Disrupt Global Cybercrime and Fraudulent Networks

Meta Platforms, Microsoft, and the U.S. Department of Justice (DoJ) have announced independent actions to tackle cybercrime and disrupt services that enable scams, fraud, and phishing attacks. To that end, Microsoft’s Digital Crimes Unit (DCU) said it seized 240 fraudulent

PyPI Attack: ChatGPT, Claude Impersonators Deliver JarkaStealer via Python Libraries

Cybersecurity researchers have discovered two malicious packages uploaded to the Python Package Index (PyPI) repository that impersonated popular artificial intelligence (AI) models like OpenAI ChatGPT and Anthropic Claude to deliver an information stealer called JarkaStealer. The packages, named gptplus and

Warning: Over 2,000 Palo Alto Networks Devices Hacked in Ongoing Attack Campaign

As many as 2,000 Palo Alto Networks devices are estimated to have been compromised as part of a campaign abusing the newly disclosed security flaws that have come under active exploitation in the wild. According to statistics shared by the

Chinese APT Gelsemium Targets Linux Systems with New WolfsBane Backdoor

The China-aligned advanced persistent threat (APT) actor known as Gelsemium has been observed using a new Linux backdoor dubbed WolfsBane as part of cyber attacks likely targeting East and Southeast Asia. That’s according to findings from cybersecurity firm ESET based

10 Most Impactful PAM Use Cases for Enhancing Organizational Security

Privileged access management (PAM) plays a pivotal role in building a strong security strategy. PAM empowers you to significantly reduce cybersecurity risks, gain tighter control over privileged access, achieve regulatory compliance, and reduce the burden on your IT team.  As

North Korean Front Companies Impersonate U.S. IT Firms to Fund Missile Programs

Threat actors with ties to the Democratic People’s Republic of Korea (DPRK) are impersonating U.S.-based software and technology consulting businesses in order to further their financial objectives as part of a broader information technology (IT) worker scheme. “Front companies, often

Cyber Story Time: The Boy Who Cried “Secure!”

As a relatively new security category, many security operators and executives I’ve met have asked us “What are these Automated Security Validation (ASV) tools?” We’ve covered that pretty extensively in the past, so today, instead of covering the “What is