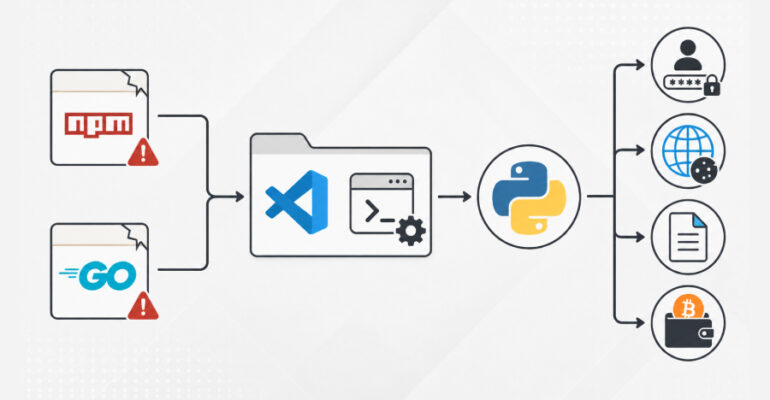
Hijacked npm and Go Packages Use VS Code Tasks to Deploy Python Infostealer

Cybersecurity researchers have uncovered two hijacked npm packages and a cluster of Go packages that are designed to deploy a Python-based information stealer on compromised Windows, Linux, and macOS hosts. “This attack avoids the most common npm execution paths through

Ukraine Says Russian Intelligence Used Fake Support Texts to Steal Messaging Credentials

The Security Service of Ukraine (SSU) said it, together with the U.S. Federal Bureau of Investigation (FBI), uncovered a long-running campaign orchestrated by Russian intelligence services to break into the messaging accounts of government officials, military personnel, politicians, and activists

OpenAI Previews GPT-5.6 Sol With Restricted Access and Stronger Cyber Safeguards

OpenAI on Friday released three versions of GPT-5.6, called Sol, Terra, and Luna, as a limited preview to a small number of companies as part of an ongoing engagement with the U.S. government. While Sol is the latest flagship model

FBI Warns Russian Intelligence Hackers Target Signal Backup Recovery Keys

The FBI and CISA have updated their March warning about Russian intelligence phishing Signal accounts, and the operators have added a step: they now coax targets into handing over their Signal Backup Recovery Key. Hand it over once, and the attacker can

New SharkLoader Malware Deploys Cobalt Strike in StrikeShark Cyberattacks

A newly discovered cyber attack campaign has been observed delivering a previously undocumented malware family called SharkLoader that acts as a loader for deploying Cobalt Strike Beacon on compromised hosts. Kaspersky, which is tracking the activity under the moniker StrikeShark,

Chinese-Speaking APT Deploys New TinyRCT Backdoor in Southeast Asia Campaign

A Chinese-speaking advanced persistent threat (APT) actor has been linked to a new custom backdoor called TinyRCT as part of cyber attacks aimed at government entities and critical infrastructure in Southeast Asia. The activity, particularly aimed at state-owned enterprises in

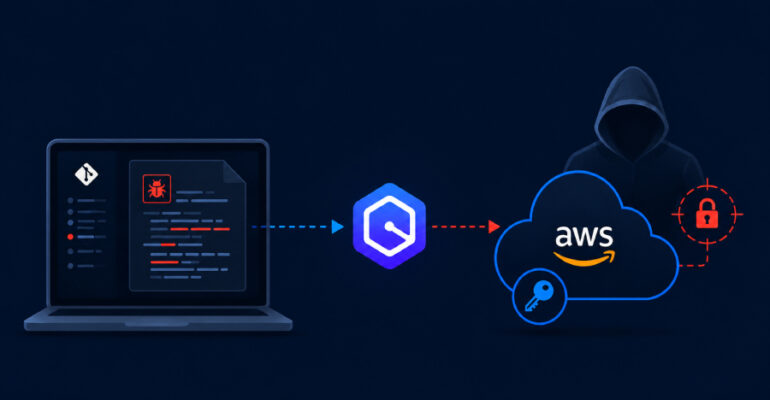
Amazon Q Developer Flaw Could Let Malicious Repos Run Code via MCP Configs

A high-severity flaw in Amazon Q Developer let a malicious repository run commands and steal a developer’s cloud credentials. The path was short: a developer opens the repo, trusts the workspace, and Amazon Q does the rest. Amazon has patched

New Linux pedit COW Exploit Enables Root Access by Poisoning Cached Binaries

A flaw in the Linux kernel’s traffic-control subsystem can let a local unprivileged user gain root on affected systems. CVE-2026-46331, nicknamed “pedit COW,” is an out-of-bounds write in the packet-editing action (act_pedit) that corrupts shared page-cache memory. A public, working exploit appeared

CISA Adds Exploited PTC Windchill RCE Flaw to KEV as Web Shell Attacks Continue

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added a critical remote code execution vulnerability impacting PTC Windchill PDMlink and PTC FlexPLM enterprise Product Data Management (PDM) and Product Lifecycle Management (PLM) software to its Known Exploited Vulnerabilities

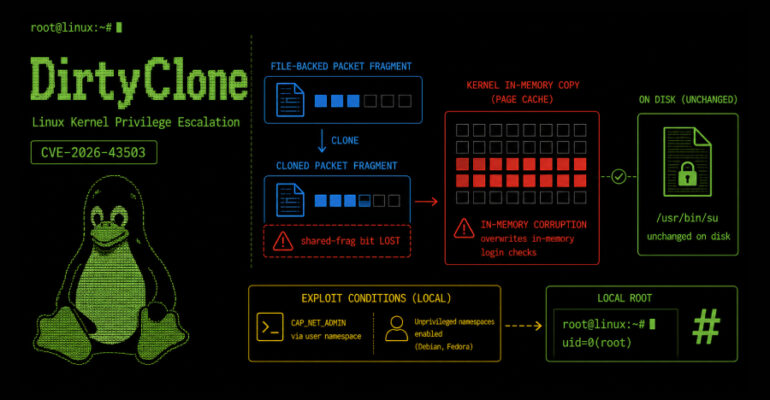
New DirtyClone Linux Kernel Flaw Lets Local Users Gain Root via Cloned Packets

DirtyClone is a new Linux kernel privilege escalation in the DirtyFrag family. JFrog Security Research published a working exploit walkthrough for the flaw on June 25, the first public demonstration for this variant. Tracked as CVE-2026-43503 (CVSS 8.8), it lets a local user corrupt