Guardian Agents: The Next Layer of Identity Governance

AI agents are moving through enterprise environments, inheriting permissions, traversing systems, and executing decisions at machine speed with minimal oversight. The identity infrastructure built to govern human access wasn’t designed for autonomous actors, and the gap between what enterprises are
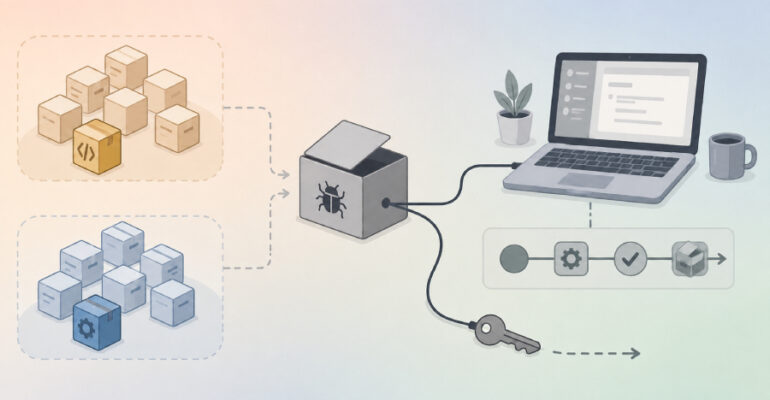
Miasma Malware Targets npm Packages and GitHub Actions in Supply Chain Attack

Cybersecurity researchers have flagged yet another evolution of the supply chain attack linked to the Mini Shai-Hulud, Miasma, and Hades malware family that has compromised a new set of npm packages, even as it has propagated to the Go ecosystem.

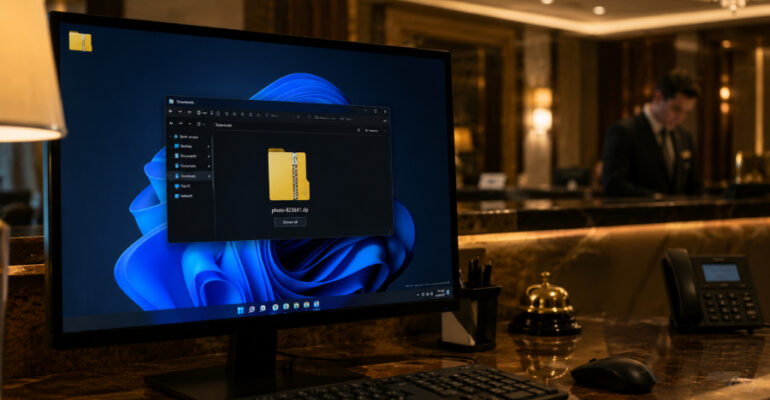
Microsoft Warns of Photo ZIP Phishing Campaign Targeting Hotels with Node.js Implant

An active phishing campaign has been targeting hotel and other hospitality organizations across Europe and Asia since April 2026, using photo-themed ZIP files to drop a Node.js implant and dig into front-desk machines, Microsoft says. The company has not attributed the activity

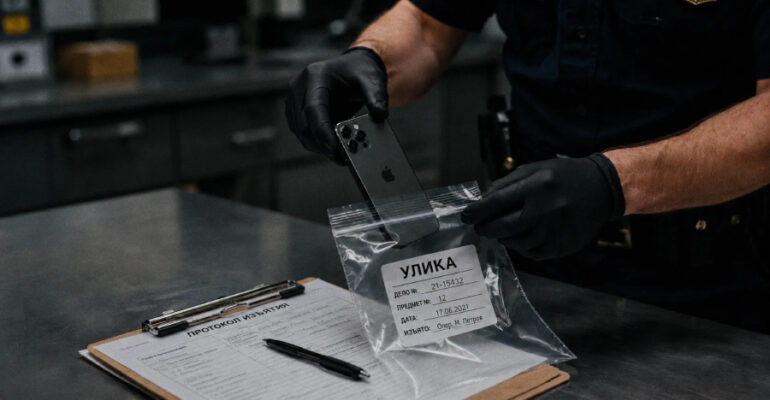
Russia Used Cellebrite on Jailed Activist’s iPhone Months After Sales Cutoff

Russian authorities used Cellebrite’s UFED forensic tools to break into the iPhone of detained opposition activist Andrey Pivovarov in June 2021, three months after Cellebrite said it would stop selling its tools and services to Russia and Belarus. The finding,

Google Details Turla’s New STOCKSTAY Backdoor Used in Ukraine Espionage Attacks

The Russian state-sponsored threat actor known as Turla has been attributed to a previously undocumented .NET backdoor called STOCKSTAY that has been deployed against government and military organizations in Ukraine, and entities that have an interest in Italian foreign policy.

Chrome Ad Blocker with 10M+ Installs Found with Dormant Script Injection Capability

An analysis of a popular Google Chrome ad block extension for YouTube has uncovered the ability to execute arbitrary JavaScript code. According to Island, the extension, named Adblock for YouTube (ID: cmedhionkhpnakcndndgjdbohmhepckk), has more than 10 million installs and carries

ThreatsDay Bulletin: Smart TV Proxyware, 24-Year curl Bug, AI Crime Forums + 13 More Stories

It’s dumb out there again. This week has the usual smell of prod on fire and nobody wanting to admit who left the door open — old creds still working, trusted apps doing sketchy crap, browser tricks jumping the fence,

Surviving the Mythos Era: Richard Bejtlich on the Case for NDR

Despite the abundance of telemetry at analysts’ disposal, many security operations teams struggle to answer a few basic questions during incident investigation: What happened? What evidence do we have? How do we know we’re seeing it all, in context? Answering

New Gaslight macOS Malware Uses Prompt Injection to Disrupt AI-Assisted Analysis

A previously undocumented Rust-based macOS implant and information stealer has been found to embed a prompt injection payload designed to trick a malware analyst’s artificial intelligence (AI) tools and trick it into aborting or refusing an analysis of the artifact.

New Mistic Backdoor Linked to KongTuke in ClickFix and ModeloRAT Campaigns

A new, stealthy backdoor named Mistic has been deployed as part of suspected financially motivated attacks aimed at multiple organizations spanning insurance, education, IT, and professional services sectors since April 2026. According to Symantec and Carbon Black’s Threat Hunter Team,