
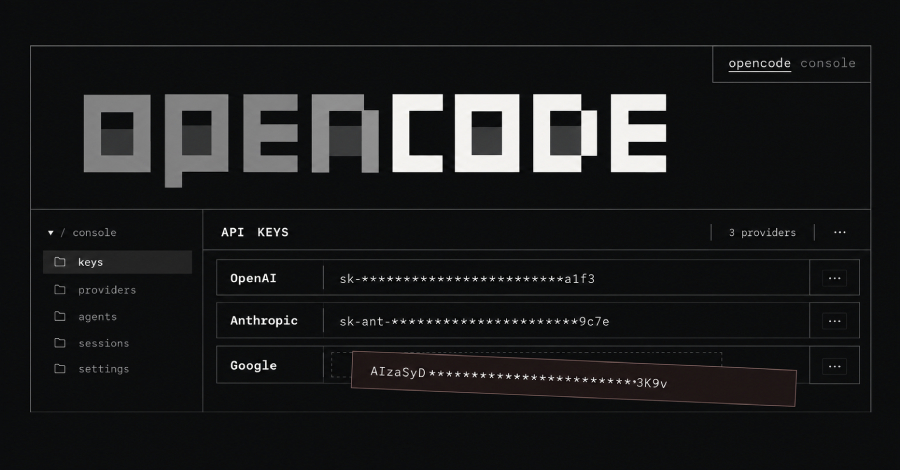
An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users had saved in OpenCode Console, the company said.
Console is OpenCode’s optional hosted service: a workspace saves its own OpenAI, Anthropic, or Google key there, and Console uses that key to call the provider so team members can use the models without…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment