
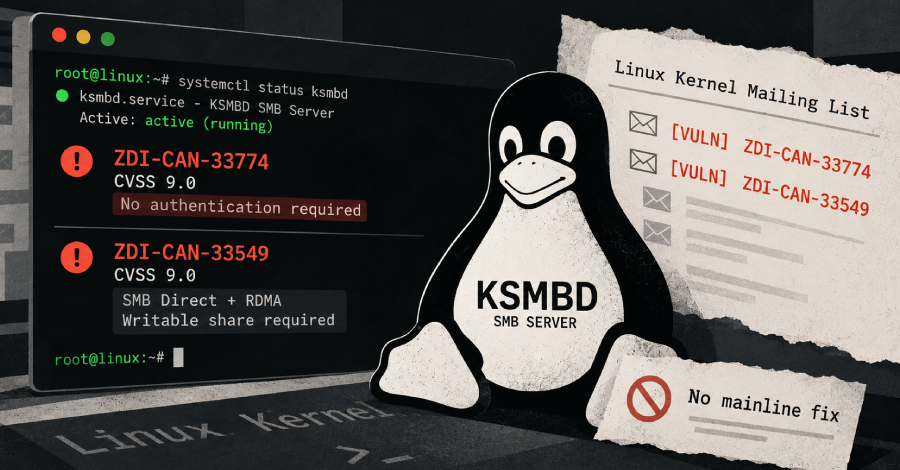
Linux servers running KSMBD, the kernel’s built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro’s Zero Day Initiative, with no fix yet in the mainline kernel.
One of them, ZDI-CAN-33774, can be triggered before any network authentication. The other, ZDI-CAN-33549, requires the SMB Direct transport and an RDMA-capable network…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment