Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes

Cybersecurity researchers have disclosed details of a “human-operated phishing platform” that impersonates advertising products for artificial intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI ChatGPT, Perplexity, Meta Muse, and Manus. The products, which claim to offer campaign optimization, spend
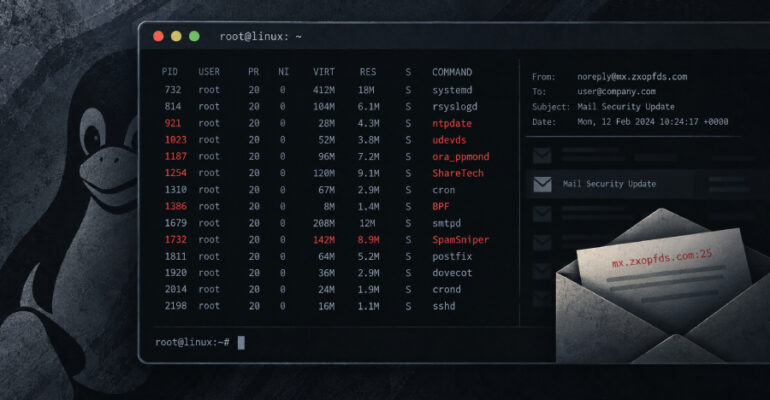
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan

Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services and seemingly legitimate processes to blend in and evade detection. Threat actors are known to name their malicious software after

LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings

A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker’s code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows before it runs a macro.

Wikimedia Says OpenAI Agents Tried to Compromise Etherpad and Use Wiki Tools as Proxies

The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool, and edit Wikipedia pages. “The unauthorized bot activities included edits

Welcome to the Jungle: What We Found Inside 15,465 Public MCP Servers

In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and enterprises plugged them into agent

Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports

Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security flaws in the code of projects such as Go, Angular,

Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products

A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product’s web application root directory. The attacker must already know a file’s exact name

FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach

The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees. That’s according to a report from Reuters, citing

Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account

Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population register, the country’s digitalization ministry said on October 5. They used a private Danish company’s lawful

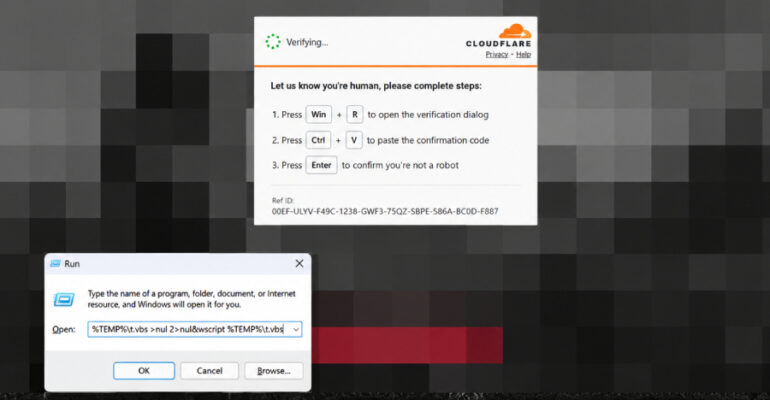
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits

A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the