
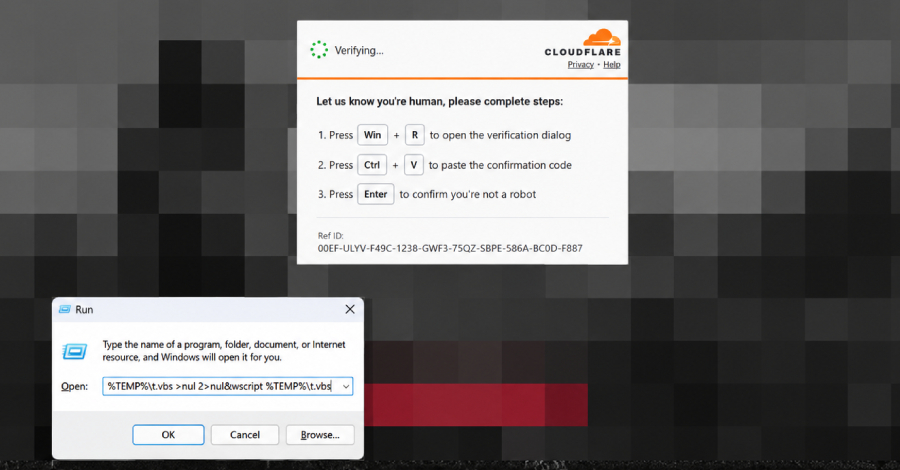
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache.
“Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file,” the Microsoft Threat Intelligence team said in a post on X….
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment