iOS 26.5 Brings Default End-to-End Encrypted RCS Messaging Between iPhone and Android

Apple on Monday officially released iOS 26.5 with support for end-to-end encryption (E2EE) to Rich Communication Services (RCS) in beta as part of a “cross-industry effort” to replace traditional SMS with a more secure alternative. To that end, E2EE RCS
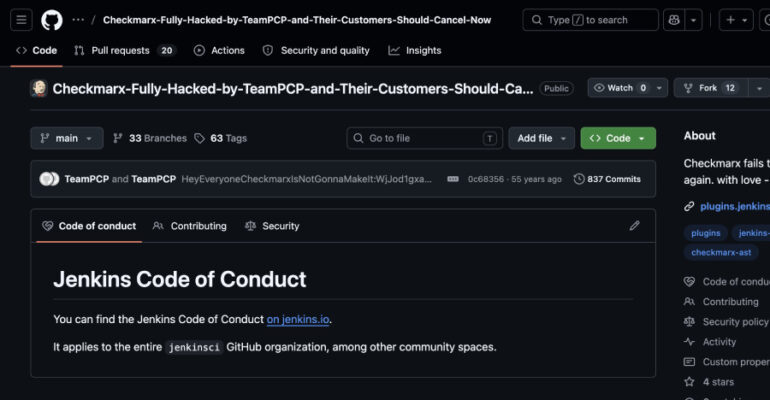
TeamPCP Compromises Checkmarx Jenkins AST Plugin Weeks After KICS Supply Chain Attack

Checkmarx has confirmed that a modified version of the Jenkins AST plugin was published to the Jenkins Marketplace. “If you are using Checkmarx Jenkins AST plugin, you need to ensure that you are using the version 2.0.13-829.vc72453fa_1c16 that was published

cPanel CVE-2026-41940 Under Active Exploitation to Deploy Filemanager Backdoor

A threat actor named Mr_Rot13 has been attributed to the exploitation of a recently disclosed critical cPanel flaw to deploy a backdoor codenamed Filemanager on compromised environments. The attack exploits CVE-2026-41940, a vulnerability impacting cPanel and WebHost Manager (WHM) that

Hackers Used AI to Develop First Known Zero-Day 2FA Bypass for Mass Exploitation

Google on Monday disclosed that it identified an unknown threat actor using a zero-day exploit that it said was likely developed with an artificial intelligence (AI) system, marking the first time the technology has been put to use in the

⚡ Weekly Recap: Linux Rootkit, macOS Crypto Stealer, WebSocket Skimmers and More

Rough Monday. Somebody poisoned a trusted download again, somebody else turned cloud servers into public housing, and a few crews are still getting into boxes with bugs that should’ve died years ago — the same old holes, same lazy access

Your Purple Team Isn’t Purple — It’s Just Red and Blue in the Same Room

Defending a network at 2 am looks a lot like this: an analyst copy-pasting a hash from a PDF into a SIEM query. A red team script is being rewritten by hand so the blue team can use it. A

Fake OpenAI Privacy Filter Repo Hits #1 on Hugging Face, Draws 244K Downloads

A malicious Hugging Face repository managed to take a spot in the platform’s trending list by impersonating OpenAI’s Privacy Filter open-weight model to deliver a Rust-based information stealer to Windows users. The project, named Open-OSS/privacy-filter, masqueraded as its legitimate counterpart,

Ollama Out-of-Bounds Read Vulnerability Allows Remote Process Memory Leak

Cybersecurity researchers have disclosed a critical security vulnerability in Ollama that, if successfully exploited, could allow a remote, unauthenticated attacker to leak its entire process memory. The out-of-bounds read flaw, which likely impacts over 300,000 servers globally, is tracked as

cPanel, WHM Release Fixes for Three New Vulnerabilities — Patch Now

cPanel has released updates to address three vulnerabilities in cPanel and Web Host Manager (WHM) that could be exploited to achieve privilege escalation, code execution, and denial-of-service. The list of vulnerabilities is as follows – CVE-2026-29201 (CVSS score: 4.3) –

TCLBANKER Banking Trojan Targets Financial Platforms via WhatsApp and Outlook Worms

Threat hunters have flagged a previously undocumented Brazilian banking trojan dubbed TCLBANKER that’s capable of targeting 59 banking, fintech, and cryptocurrency platforms. The activity is being tracked by Elastic Security Labs under the moniker REF3076. The malware family is assessed