BengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support Scams

Cybersecurity researchers have disclosed details of a sprawling search engine optimization (SEO) poisoning campaign that paves the way for malware deployment and tech support scams. The campaign, discovered by the DFIR Report in March 2026, has been codenamed BengalSEO. It
Grindr to Pay £26 Million to Settle U.K. Claims Over HIV Status Data Sharing

Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it shared users’ personal information, including their HIV status, with third-parties. Grindr, which is the largest LGBTQ+ dating

PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution

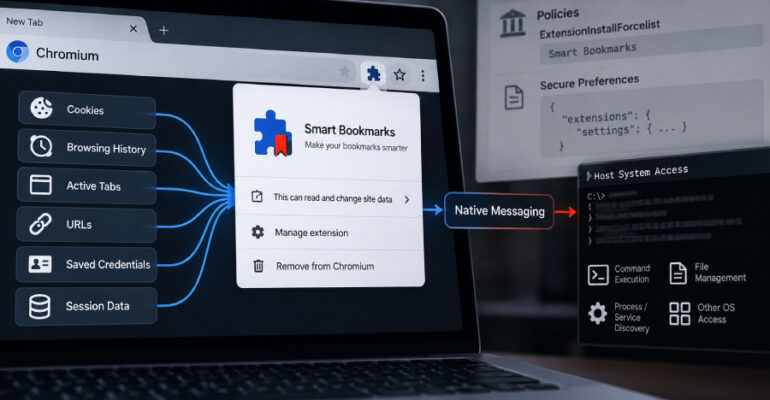
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. “Requiring prior administrative or code execution access, its installer injects the extension directly into Chrome/Edge profiles, bypassing

Fake IT Calls Target Executives in Microsoft 365 Data Theft and Extortion Attacks

Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that’s targeting Microsoft 365 and other software-as-a-service (SaaS) offerings through information technology (IT) help desk vishing, adversary-in-the-middle (AitM) token theft, and residential-proxy sign-ins. The activity, which

⚡ Weekly Recap: Chrome 0-Day, Router Hijacks, Coder Supply Chain Attack and More

Turning off email images should at least stop the pictures. This week, attackers had a workaround: a scannable QR code built out of text. It still appears, even with images blocked. A small detail, but an annoying one if that

Your Cloud Security Checklist Doesn’t Work the Way You Think It Does

If managing security across multiple cloud providers wasn’t hard enough, each one fails in a different way. For the 2026 Cloud Security Index, Intruder analyzed misconfiguration data from 3,000 organizations across AWS, Azure, and Google Cloud and found that risk

Rogue ScreenConnect Clients Spread Four-Stage VBScript Chain to Newly Connected Hosts

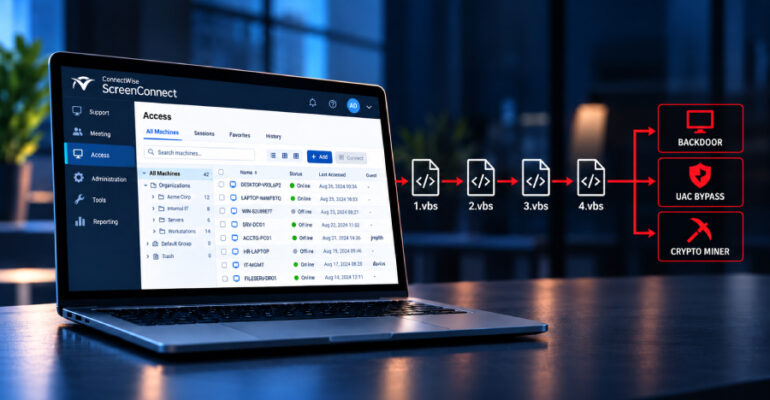
Cybersecurity researchers have disclosed details of worm-like activity that abuses ConnectWise ScreenConnect to distribute a malicious Visual Basic Script (VBScript) payload to newly connected systems. According to Huntress, three unrelated incidents have been found to use diverse initial access methods,

Telerik UI Padding-Oracle Bug Chained to Unauthenticated RCE — Public Exploit Released

A TantoSec proof-of-concept turns an AES-CBC “padding oracle” in Telerik UI for ASP.NET AJAX into unauthenticated remote code execution — but only against applications in a specific non-default configuration, and Progress patched the chain in July. There are no confirmed

N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw

Every on-premises N-central build below 2026.3.1.14 — including servers updated to Hotfix 3 a day earlier — needs Hotfix 4. N-able’s incident notice says the flaw has been exploited in the wild; its release notes say that is unconfirmed. N-able

JSCeal Malware Can Bypass Google Authentication Using Stolen Session Cookies

Cybersecurity researchers have unpacked JSCeal, a sophisticated compiled V8 JavaScript (JSC) malware with credential harvesting, surveillance, and traffic-interception capabilities. “The payloads are protected with javascript-obfuscator, using multiple techniques including RC4-protected strings, control-flow flattening, proxy functions, and operation wrappers,” Check Point