Russian-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine Attack

The Russian state-sponsored hacking group Sandworm teamed up with another threat actor to carry out a destructive wiping attack targeting a Ukrainian logistics company last year. According to ESET, the attack involved UAC-0099 (aka Earth Sirrush) obtaining initial access to
Critical Flaw in Python’s Popular Pillow Image Library Allows Code Execution via a Crafted Image

Pillow, the most widely used image library for Python, can be made to run operating system commands on a server by specifying the name of a file it is told to open. The flaw, CVE-2026-112900, is in the way Pillow handles

Critical x402 SDK Flaw Could Let Malicious APIs Drain AI Agents’ Token Balances

AI agents paying for API calls with the x402 SDKs could sign a payment for their full balance of a supported token if a malicious API asked for it, security firm V12 said on October 22. The cause was the SDKs’ default client, which

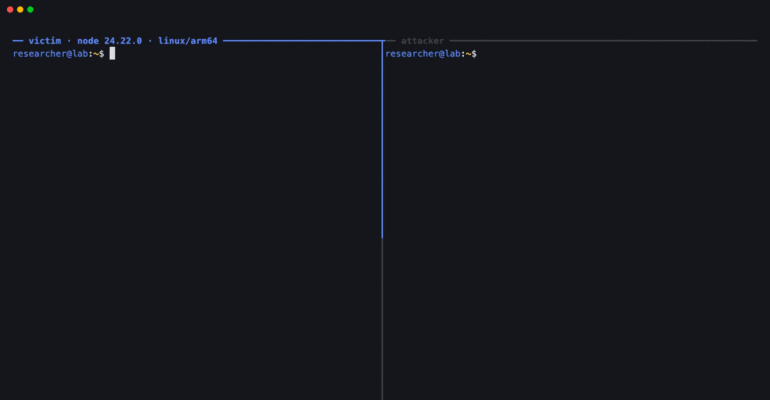
Researchers Demonstrate Node2Shell RCE Exploit on Node.js Build Using Crafted Brotli Data

Malicious Brotli data can make an application on an official build of Node.js run attacker-supplied code, security researchers at Imperva have demonstrated. Their “Node2Shell” proof of concept ran code on the official Node.js 24.22.0 image for Linux arm64, with no debugger

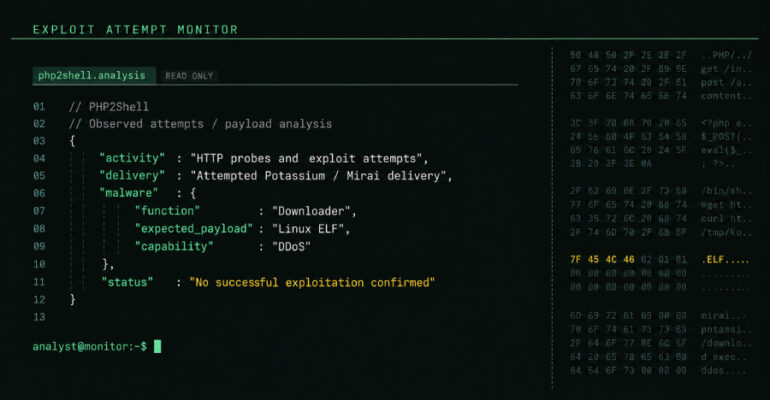
PHP2Shell Exploit Attempts Hit Millions as Attackers Try to Deploy Mirai Malware

Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges that weaponizing the flaws may be harder than previously thought. The attacks

Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

Attackers are exploiting a zero-day SQL injection flaw in Arista’s VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw lets anyone who can log in to the orchestrator, even with a

eMudhra to Exit Global SSL/TLS Business After 8 Intermediate CA Keys Found Easily Guessable

eMudhra, an Indian certificate authority (CA), will withdraw from its global SSL/TLS certificate business, its board decided on Thursday. The decision came five days after a researcher reported recovering the private keys of eight of its intermediate CA certificates. eMudhra said it will

ThreatsDay: AI Secrets Leak, PingCAP Source Theft, Signal Hang-Up Flaw, Laravel Auth Bypass + 21 More

This week has already been rough for cybersecurity. Critical PHP and GitLab RCE flaws, serious Linux security bugs, compromised eMudhra certificates, a Node.js RCE flaw, a hacked LiteLLM release, and hundreds of hijacked Tor relays. That’s a lot to deal

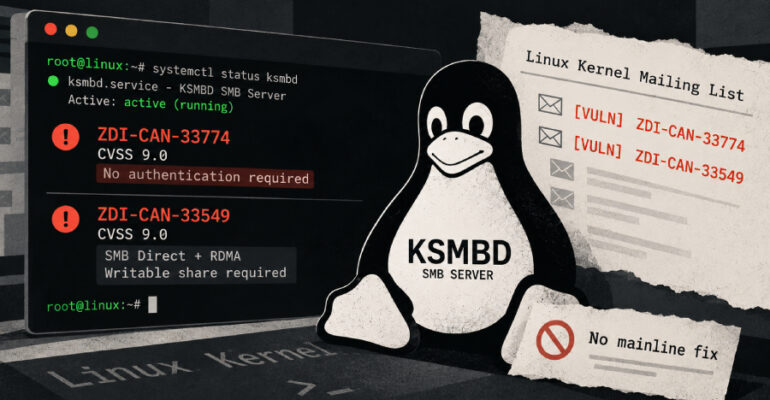
Two CVSS 9.0 Linux KSMBD RCE Flaws Disclosed on Public Mailing Lists Before Kernel Fixes

Linux servers running KSMBD, the kernel’s built-in SMB server, are exposed to two publicly reported remote code execution flaws rated 9.0 by Trend Micro’s Zero Day Initiative, with no fix yet in the mainline kernel. One of them, ZDI-CAN-33774, can be

Meta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy Violations

Social media giant Meta was ordered to pay 25 billion in penalties by a New Mexico court on Wednesday as part of a data privacy lawsuit that sprang from the company’s Cambridge Analytica data scandal, which came to light in