OPSEC Failure Exposes Coquettte’s Malware Campaigns on Bulletproof Hosting Servers

A novice cybercrime actor has been observed leveraging the services of a Russian bulletproof hosting (BPH) provider called Proton66 to facilitate their operations. The findings come from DomainTools, which detected the activity after it discovered a phony website named cybersecureprotect[.]com
CERT-UA Reports Cyberattacks Targeting Ukrainian State Systems with WRECKSTEEL Malware

The Computer Emergency Response Team of Ukraine (CERT-UA) has revealed that no less than three cyber attacks were recorded against state administration bodies and critical infrastructure facilities in the country with an aim to steal sensitive data. The campaign, the

Critical Flaw in Apache Parquet Allows Remote Attackers to Execute Arbitrary Code

A maximum severity security vulnerability has been disclosed in Apache Parquet’s Java Library that, if successfully exploited, could allow a remote attacker to execute arbitrary code on susceptible instances. Apache Parquet is a free and open-source columnar data file format

Microsoft Warns of Tax-Themed Email Attacks Using PDFs and QR Codes to Deliver Malware

Microsoft is warning of several phishing campaigns that are leveraging tax-related themes to deploy malware and steal credentials. “These campaigns notably use redirection methods such as URL shorteners and QR codes contained in malicious attachments and abuse legitimate services like

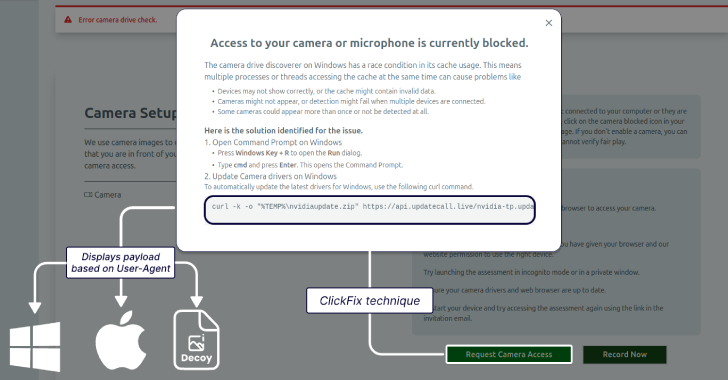
Lazarus Group Targets Job Seekers With ClickFix Tactic to Deploy GolangGhost Malware

The North Korean threat actors behind Contagious Interview have adopted the increasingly popular ClickFix social engineering tactic to lure job seekers in the cryptocurrency sector to deliver a previously undocumented Go-based backdoor called GolangGhost on Windows and macOS systems. The

AI Threats Are Evolving Fast — Learn Practical Defense Tactics in this Expert Webinar

The rules have changed. Again. Artificial intelligence is bringing powerful new tools to businesses. But it’s also giving cybercriminals smarter ways to attack. They’re moving quicker, targeting more precisely, and slipping past old defenses without being noticed. And here’s the

AI Adoption in the Enterprise: Breaking Through the Security and Compliance Gridlock

AI holds the promise to revolutionize all sectors of enterpriseーfrom fraud detection and content personalization to customer service and security operations. Yet, despite its potential, implementation often stalls behind a wall of security, legal, and compliance hurdles. Imagine this all-too-familiar

Google Patches Quick Share Vulnerability Enabling Silent File Transfers Without Consent

Cybersecurity researchers have disclosed details of a new vulnerability impacting Google’s Quick Share data transfer utility for Windows that could be exploited to achieve a denial-of-service (DoS) or send arbitrary files to a target’s device without their approval. The flaw,

Triada Malware Preloaded on Counterfeit Android Phones Infects 2,600+ Devices

Counterfeit versions of popular smartphone models that are sold at reduced prices have been found to be preloaded with a modified version of an Android malware called Triada. “More than 2,600 users in different countries have encountered the new version

Legacy Stripe API Exploited to Validate Stolen Payment Cards in Web Skimmer Campaign

Threat hunters are warning of a sophisticated web skimmer campaign that leverages a legacy application programming interface (API) from payment processor Stripe to validate stolen payment information prior to exfiltration. “This tactic ensures that only valid card data is sent