Europol Dismantles Kidflix With 72,000 CSAM Videos Seized in Major Operation

In one of the largest coordinated law enforcement operations, authorities have dismantled Kidflix, a streaming platform that offered child sexual abuse material (CSAM). “A total of 1.8 million users worldwide logged on to the platform between April 2022 and March
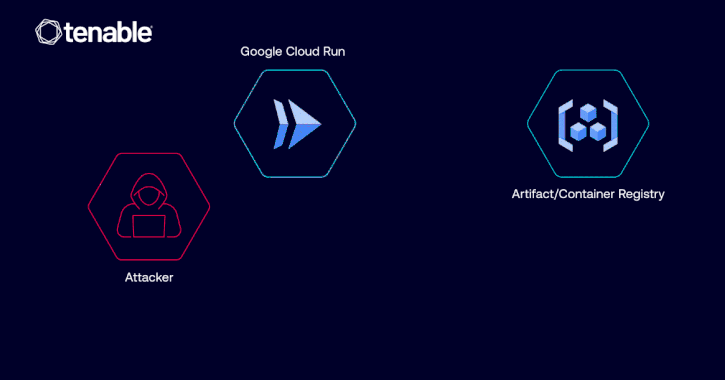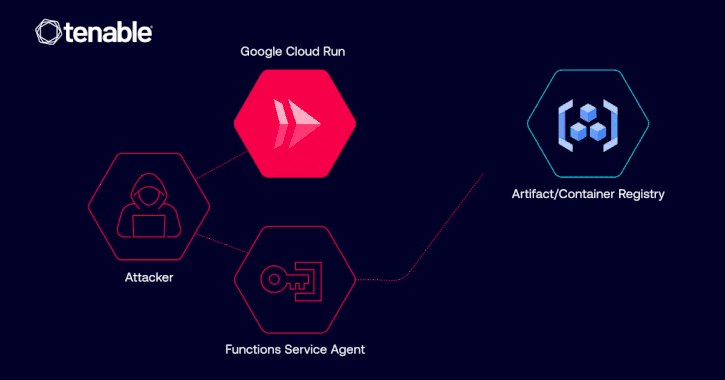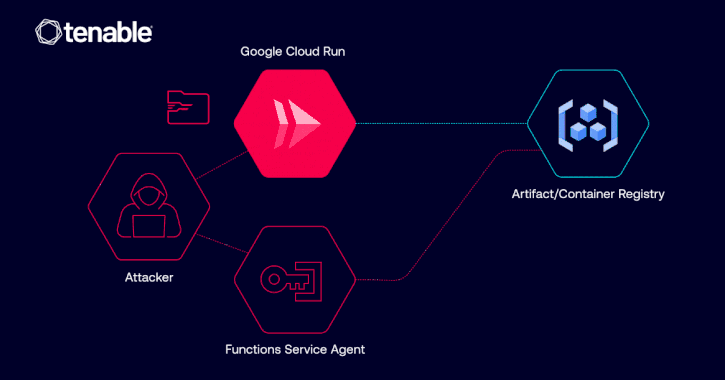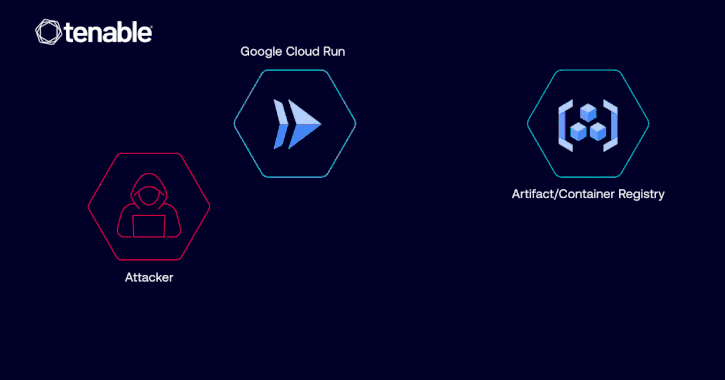
Google Fixed Cloud Run Vulnerability Allowing Unauthorized Image Access via IAM Misuse

Cybersecurity researchers have disclosed details of a now-patched privilege escalation vulnerability in Google Cloud Platform (GCP) Cloud Run that could have allowed a malicious actor to access container images and even inject malicious code. “The vulnerability could have allowed such

Helping Your Clients Achieve NIST Compliance: A Step by Step Guide for Service Providers

Introduction As the cybersecurity landscape evolves, service providers play an increasingly vital role in safeguarding sensitive data and maintaining compliance with industry regulations. The National Institute of Standards and Technology (NIST) offers a comprehensive set of frameworks that provide a

Outlaw Group Uses SSH Brute-Force to Deploy Cryptojacking Malware on Linux Servers

Cybersecurity researchers have shed light on an “auto-propagating” cryptocurrency mining botnet called Outlaw (aka Dota) that’s known for targeting SSH servers with weak credentials. “Outlaw is a Linux malware that relies on SSH brute-force attacks, cryptocurrency mining, and worm-like propagation

How SSL Misconfigurations Impact Your Attack Surface

When assessing an organization’s external attack surface, encryption-related issues (especially SSL misconfigurations) receive special attention. Why? Their widespread use, configuration complexity, and visibility to attackers as well as users make them more likely to be exploited.  This highlights how important

FIN7 Deploys Anubis Backdoor to Hijack Windows Systems via Compromised SharePoint Sites

The financially motivated threat actor known as FIN7 has been linked to a Python-based backdoor called Anubis (not to be confused with an Android banking trojan of the same name) that can grant them remote access to compromised Windows systems.

New Malware Loaders Use Call Stack Spoofing, GitHub C2, and .NET Reactor for Stealth

Cybersecurity researchers have discovered an updated version of a malware loader called Hijack Loader that implements new features to evade detection and establish persistence on compromised systems. “Hijack Loader released a new module that implements call stack spoofing to hide

Over 1,500 PostgreSQL Servers Compromised in Fileless Cryptocurrency Mining Campaign

Exposed PostgreSQL instances are the target of an ongoing campaign designed to gain unauthorized access and deploy cryptocurrency miners. Cloud security firm Wiz said the activity is a variant of an intrusion set that was first flagged by Aqua Security

Enterprise Gmail Users Can Now Send End-to-End Encrypted Emails to Any Platform

On the 21st birthday of Gmail, Google has announced a major update that allows enterprise users to send end-to-end encrypted (E2EE) to any user in any email inbox in a few clicks. The feature is rolling out starting today in

Lucid PhaaS Hits 169 Targets in 88 Countries Using iMessage and RCS Smishing

A new sophisticated phishing-as-a-service (PhaaS) platform called Lucid has targeted 169 entities in 88 countries using smishing messages propagated via Apple iMessage and Rich Communication Services (RCS) for Android. Lucid’s unique selling point lies in its weaponizing of legitimate communication