Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers

Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports from Kaspersky. The cybersecurity vendor said it has identified attacks mounted by NightEagle (aka APT-Q-95),
One Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and Claude

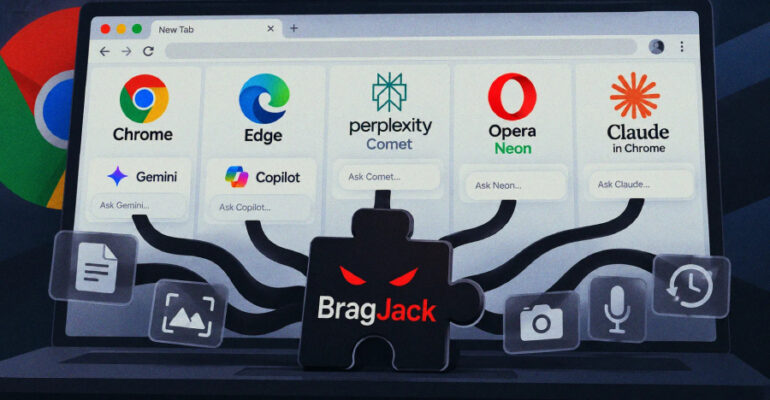
Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in Chrome, Perplexity Comet, Microsoft Edge, Opera Neon and the Claude in Chrome extension. Once the

Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories

Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories. Before the repository spread, the assistant recommended software that the attacker had poisoned, and the recommendation was

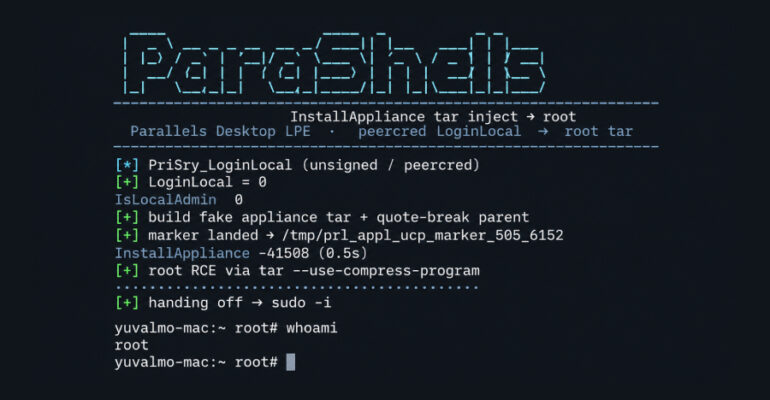
Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install Fix

Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac, software company JFrog said this week. The attack needs code already running on the machine

N0va Phishkit Targets US and EU Businesses: A New Challenge for Identity Security

N0va is targeting organizations across North America and Europe with phishing campaigns that impersonate trusted services and abuse legitimate authentication flows. Successful attacks can give threat actors access to valid accounts without relying on obvious malware activity. From there, a

Google Patches Pixel Modem Flaw Amid Signs of Limited Targeted Exploitation

Google has disclosed that a high-severity security flaw in its Pixel Cellular Modem has come under exploitation in the wild. The vulnerability, tracked as CVE-2026-58704 (CVSS score: 8.0), is a privilege escalation flaw. “In Cellular Modem, there is a possible

Threat Intelligence Alone Won’t Close the Exploitation Gap

A leaked credential shows up in a criminal marketplace, or a vulnerability gets a disclosure advisory, and either one can be weaponized against a real target before most security teams have triaged the alert. Attackers are combining that kind of

Acronis cPanel Backup Plugin Vulnerability Exploited in Targeted Attacks

Acronis has warned that a high-severity security flaw in its Backup plugin for cPanel and Web Host Manager (WHM) deployments has been exploited in the wild. The vulnerability, tracked as CVE-2026-87886 (CVSS score: 7.8), is described as a case of

Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells

Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and

Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens

A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as CVE-2026-5430 (CVSS score: 9.8/10.0), is a case of improper verification of a cryptographic signature that