KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens

Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the activity under the moniker REF9334. Active since at least May 2025, the threat actor has
Iranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists

Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran’s intelligence service uses to spy on dissidents, journalists, and activists around the world. The malware is controlled via the

BambooToken Malware Uses MQTT to Control Windows and Linux Systems

Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows and Linux systems. The emerging malware family, codenamed BambooToken, is assessed to be active since

Human Attacker Exploits Marimo RCE, Reaches SSH Bastion in Eight Seconds

With artificial intelligence (AI) shrinking the window between vulnerability discovery and exploitation and lowering the barrier to entry for bad actors, new findings from Sysdig show that skilled human operators can move just as swiftly after gaining initial access. In

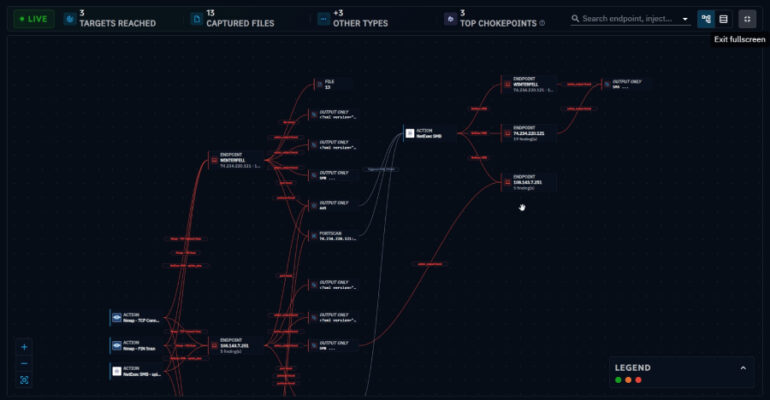
Attack Chains, Not Just Attack Surfaces: Why Testing Individual Techniques Misses the Point

Introduction Security teams have gotten pretty good at testing against what can hurt them. Can this EDR agent catch this payload? Will my organization fail the phishing simulation? Does this SIEM rule fire on this particular technique? And, in more

Mass-Scanning Campaign Exploits Vite Flaw to Extract Cloud Credentials From Exposed Dev Servers

Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an automated effort aimed at internet-exposed Vite development servers that’s designed to steal cloud credentials, configurations from Amazon Web Services

LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server

A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory published on September 14. On such servers, many customers’ sites run on a single machine,

Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution

Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The vulnerability, tracked as CVE-2026-76461, carries a CVSS score of 9.8 out of a maximum of

China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE

A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver a malicious JavaScript backdoor called GRIMWEDGE. Volexity, which is tracking the threat cluster under the

3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials

An attacker was operating inside the network of 3BB, one of Thailand’s largest broadband providers, and maintained remote control of internal machines using a legitimate management tool called MeshCentral, threat intelligence firm Hunt.io said. The company uncovered the intrusion by