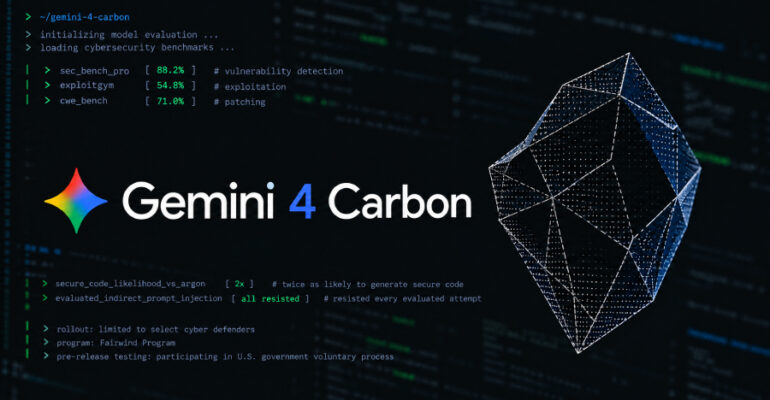
Google’s Gemini 4 Carbon Leads Benchmarks for Finding, Exploiting, and Patching Vulnerabilities

Google on Wednesday took the wraps off Gemini 4 Carbon, its latest frontier model with state-of-the-art cybersecurity and long-horizon capabilities. “It shows significant gains across coding and agentic tasks as well as across key capabilities critical for cybersecurity defense, landing
Telegram Android Flaw Lets Attackers Run Code When Users Answer Voice Calls

A flaw in Telegram for Android allowed an attacker to run code on a victim’s phone via a voice call once the victim answered, according to security startup NebuSec. The attacker needed only an ordinary Telegram account. Telegram fixed the

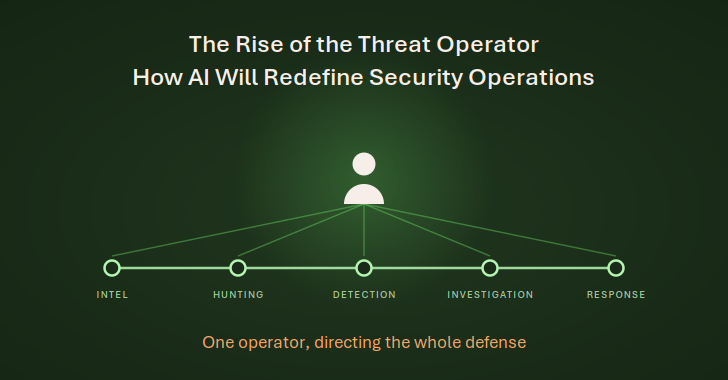
The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers

AI is beginning to take over much of the work that has traditionally defined the security analyst’s job. Investigating alerts, collecting evidence, correlating activity across tools, and executing response actions are becoming tasks that AI systems can perform on their

26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories

26,400 credentials that developers left in public code on Gitee, a Chinese code-hosting service, still worked when a researcher tested them. Anyone who copied one from that code could have used it. Independent researcher Ben Zimmermann found them by scanning

Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls

Cisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software that it said has been exploited in the wild. The vulnerability, tracked as CVE-2026-76418, is

GitHub Launches npm Firewall to Block Malicious Packages Before Installation

GitHub has announced that it’s introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time. “The firewall inspects both metadata requests and package downloads for signs of malicious activity, acting as an

Attacker Tried to Exploit Alpine Linux’s GitLab via CVSS 10.0 Flaw Its Ruby Left Open

An attacker tried to exploit a critical GitLab vulnerability on the Alpine Linux project’s own GitLab server a week after GitLab released a fix, Alpine Linux said on 28 October. The flaw, CVE-2026-97229 (CVSS score: 10.0), can let an attacker run code on

Hackers Exploited Cisco SD-WAN Flaw to Plant Malware Built to Steal Encryption Keys

Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization’s SD-WAN network. The malware, called KeyDrift, is designed to copy the keys that encrypt traffic between sites and

China-Linked Hackers Exploited VMware ESX Zero-Day to Reduce Audit Trail Visibility

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a security flaw impacting Broadcom VMware ESX to its Known Exploited Vulnerabilities (KEV) catalog, after CrowdStrike revealed that it had been weaponized by a China-nexus threat actor known as

Attackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management Interfaces

Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces. “Active exploitation has been observed targeting the Palo Alto Networks management interface exposed to the internet,” the network security company