Attackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management Interfaces

Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces. “Active exploitation has been observed targeting the Palo Alto Networks management interface exposed to the internet,” the network security company
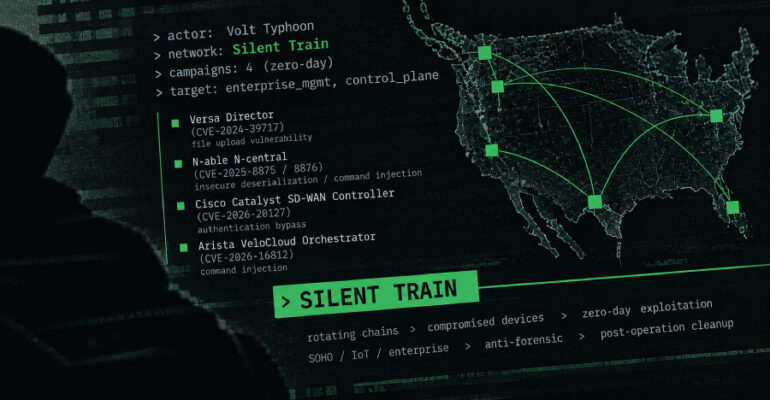
Volt Typhoon Used Covert Silent Train Network in Four Zero-Day Exploitation Campaigns

The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access. “First identified in late 2023, Silent Train

Google to Allow One-Tap Android App Installs From Approved Third-Party Stores Outside U.S.

Third-party Android app stores can now apply to Google for permission to install apps with one tap, without Android’s usual confirmation screens, and to update them in the background. To qualify, a store must pass identity checks and send Google its

Researcher Reveals How Logic Bugs Alone Cracked Microsoft Edge in $175,000 Pwn2Own Win

A chain of logic flaws, with no memory corruption, can turn a malicious web page into code running on a Windows computer outside Microsoft Edge’s sandbox, a security researcher has shown. Orange Tsai of DEVCORE published the full method on

PHP2Shell Attack Roots 25 Servers, Breaches U.S. Government-Affiliated Network

Cybersecurity researchers have disclosed details of what appears to be an artificial intelligence (AI)-assisted attack orchestrated by a suspected China-nexus threat actor that has leveraged the PHP2Shell vulnerabilities to breach exposed systems. The activity, which was observed on October 25,

Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch

Threat actors are beginning to probe for a newly patched critical vulnerability in Oracle E-Business Suite (EBS), according to threat intelligence firm Defused Cyber. The vulnerability in question is CVE-2026-101767 (CVSS score: 9.8) in the Oracle Application Object Library of

Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers

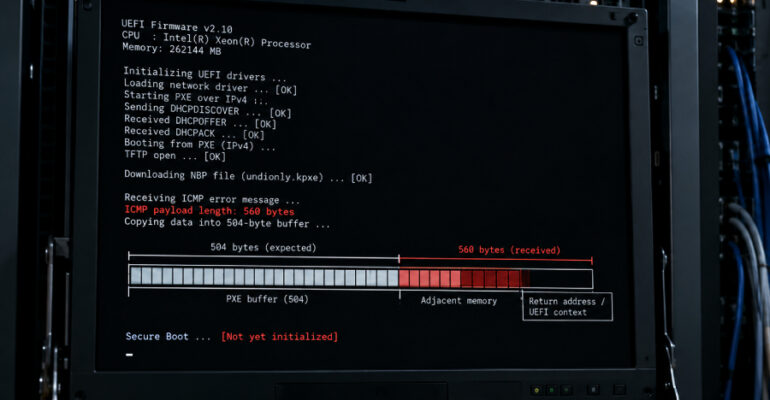
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker to run code on a machine before its operating system loads, but only while the machine is

Wazuh and AI for Enhanced SOC Workflows

Artificial Intelligence (AI) has become one of this decade’s defining technologies. From healthcare and finance to manufacturing and education, organizations increasingly rely on AI to automate repetitive tasks, uncover patterns hidden within large datasets, and support faster decision-making. Cybersecurity has

Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass

Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation. The list of eight vulnerabilities is as follows – CVE-2026-104351 (CVSS

American Organizations Under Attack: Skyw4lker Device Code Phishing Campaign Exposed

Modern phishing campaigns can compromise American businesses without relying on traditional credential theft. Attackers can abuse legitimate cloud services, authentication mechanisms, and trusted business workflows to gain access to corporate accounts while leaving fewer obvious signs behind. ANY.RUN’s analysis of