
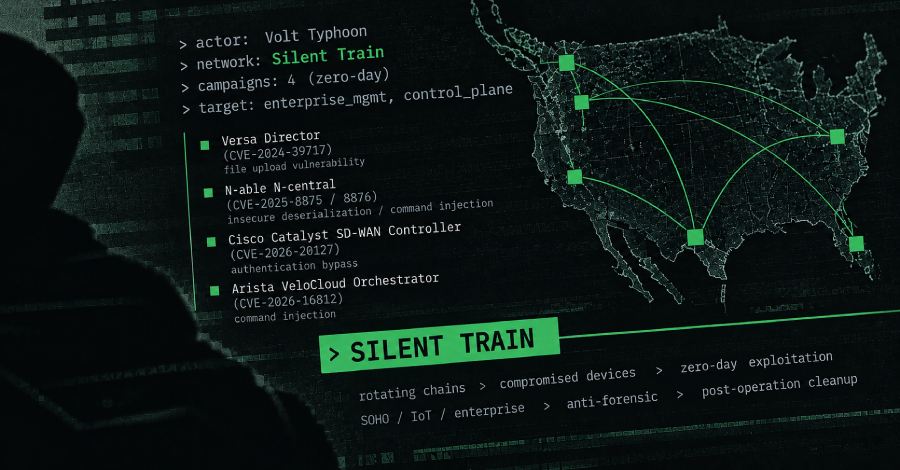
The China-nexus cyber espionage group known as Volt Typhoon has been attributed to a now-disrupted covert access network dubbed Silent Train that has been put to use for zero-day exploitation and strategic access.
“First identified in late 2023, Silent Train uses rotating chains of compromised SOHO, IoT, and enterprise infrastructure,” Lumen Technologies Black Lotus Labs said in a report shared…
Read the rest of the story at Read More
Source: The Hacker News
Recent News


Leave a Comment