





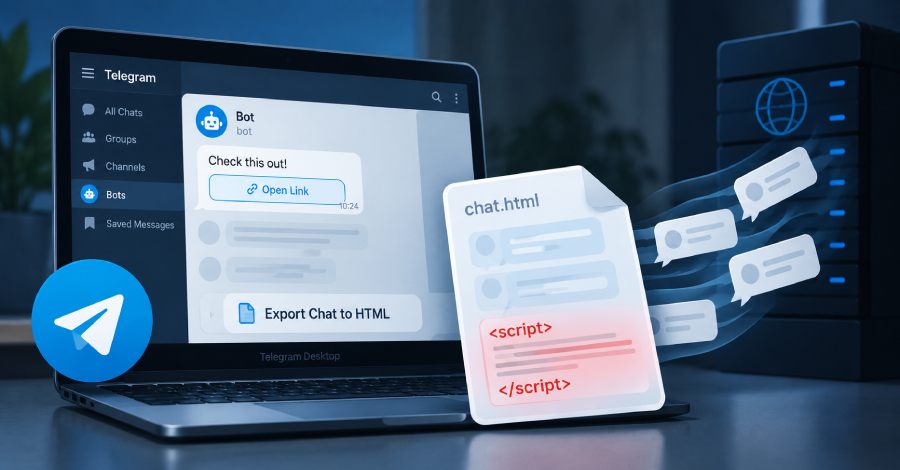
A flaw in Telegram Desktop let a bot’s message plant hidden JavaScript inside chats that users exported to HTML files, security researchers at ExPatch said in a writeup published on September 12.
In Telegram, the message looked ordinary, with a link button, and the script ran only when someone opened the export file in a web browser. It could then copy every message in that file to…
Read the rest of the story at Read More
Source: The Hacker News

Recent News


Leave a Comment